


[Dec-2024] 100% Actual FCP_FMG_AD-7.4 dumps Q&As with Explanations Verified & Correct Answers
FCP_FMG_AD-7.4 Dumps with Free 365 Days Update Fast Exam Updates
NEW QUESTION # 10
Refer to the exhibit.
An administrator is about to add the FortiGate device to FortiManager using the discovery process.
FortiManager is operating behind a NAT device, and the administrator configured the FortiManager NATed IP address under the FortiManager system administration settings.
What is the expected result?
- A. During discovery. FortiManager uses only the FortiGate serial number to establish the connection.
- B. During discovery, FortiManager sets both the FortiManager NATed IP address and NAT device IP address on FortiGate.
- C. During discovery, FortiManager sets the FortiManager NATed IP address on FortiGate.
- D. During discovery. FortiManager sets the NATed device IP address on FortiGate.
Answer: C
NEW QUESTION # 11
Exhibit.
What is true about the objects highlighted in the image?
- A. They can be set to optional or required.
- B. They are available across all ADOMs by default.
- C. They cannot be created in the global database ADOM.
- D. They can be used as variables in scripts.
Answer: D
Explanation:
The objects highlighted in the image (DMZ_SUBNET, ISP1_SUBNET, LAN_SUBNET) aremetadata variables.
* C.They can be used as variables in scripts.
* These metadata variables are placeholders that can be used in FortiManager scripts to dynamically insert specific values, enabling script flexibility and scalability across multiple devices or ADOMs.
Options A, B, and D are incorrect because:
* Asuggests optional or required settings, which do not apply to metadata variables.
* Bimplies they are available across all ADOMs by default, which is not always the case.
* Dstates they cannot be created in the global database ADOM, but metadata variables are typically managed within ADOMs and can be utilized globally based on specific configurations.
FortiManager References:
* Refer to FortiManager 7.4 Administrator Guide: Using Metadata Variables and Script Management.
NEW QUESTION # 12
Exhibit.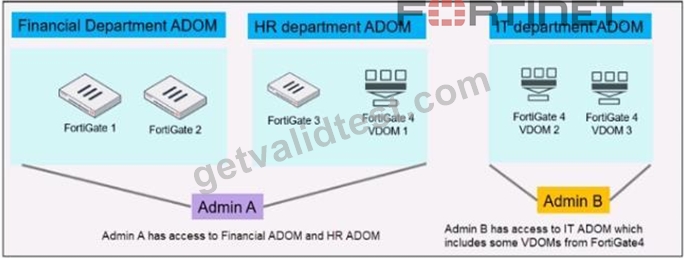
An administrator would like to create three ADOMs on FortiManager with different access levels based on departments. What two conclusions can you draw from the design shown in the exhibit? (Choose two.)
- A. The FortiManager administrator must set the ADOM device mode to Advanced
- B. An administrator with the super user profile can access all the VDOMs.
- C. The administrator must configure FortiManager in workspace normal mode.
- D. Policies and objects databases can be shared between the Financial and HR ADOMs.
Answer: A,B
Explanation:
Based on the exhibit, the FortiManager administrator is setting up three ADOMs (Administrative Domains) that correspond to different departments (Financial, HR, and IT). Each ADOM has specificFortiGate devices or VDOMs (Virtual Domains) assigned to it, with different administrators managing the ADOMs.
Explanation of Options:
* A. The FortiManager administrator must set the ADOM device mode to Advanced.
* This istrue. In FortiManager, when there areVDOMs(Virtual Domains) involved, you must set the ADOM toAdvanced modeto manage VDOMs properly. The IT department ADOM includes different VDOMs from FortiGate 4 (VDOM 2 and VDOM 3), which means the ADOM mode must be inAdvancedto support managing VDOMs separately from other ADOMs.
* B. Policies and objects databases can be shared between the Financial and HR ADOMs.
* This isfalse. By default, ADOMs are separate, and policies and objects cannot be shared between them unless they are specifically designed to do so. The exhibit shows distinct ADOMs for each department, implying no direct sharing of policies and objects between Financial and HR ADOMs.
* C. An administrator with the super user profile can access all the VDOMs.
* This istrue. A FortiManager administrator with thesuper userprofile hasfull accessto all ADOMs and VDOMs, regardless of how access is restricted for individual administrators. In this case, an admin with the super user profile could access Financial, HR, and IT ADOMs, including all the VDOMs from FortiGate 4.
* D. The administrator must configure FortiManager in workspace normal mode.
* This isfalse. There is no requirement mentioned in the exhibit or scenario that mandates using workspace normal mode. Workspace mode is more related to how configuration changes are managed (locking, editing, etc.), but it doesn't affect the creation or access control of ADOMs.
Conclusion:
* Ais correct becauseAdvanced modeis necessary for managing VDOMs within ADOMs.
* Cis correct because asuper usercan access all VDOMs and ADOMs without restrictions.
NEW QUESTION # 13
Which statement about the upgrade of ADOMs on FortiManager is true?
- A. ADOMs using global objects can be upgraded before or after upgrading the global database ADOM.
- B. You cannot import policies from a device until its FortiOS version matches the ADOM version.
- C. To ensure database consistency, you must upgrade an ADOM before you upgrade the devices in it.
- D. Upgrading the FortiManager version upgrades all existing ADOMs automatically.
Answer: C
Explanation:
* Option A: To ensure database consistency, you must upgrade an ADOM before you upgrade the devices in it.This is the correct answer. When upgrading ADOMs on FortiManager, the ADOM must be upgraded first to match the FortiOS version of the devices it manages. This is necessary to ensure compatibility and consistency between the ADOM's database schema and the FortiGate's configuration.
Explanation of Incorrect Options:
* Option B: Upgrading the FortiManager version upgrades all existing ADOMs automaticallyis incorrect because the ADOMs must be upgraded manually or individually after upgrading the FortiManager.
* Option C: You cannot import policies from a device until its FortiOS version matches the ADOM versionis incorrect because while version matching is important, it is not strictly necessary for policy import.
* Option D: ADOMs using global objects can be upgraded before or after upgrading the global database ADOMis incorrect as the order of upgrade matters to maintain compatibility.
FortiManager References:
* Refer to "FortiManager Upgrade Guide" for detailed procedures on upgrading ADOMs and devices.
NEW QUESTION # 14
What will be the result of reverting to a previous revision version in the revision history?
- A. It will generate a new version ID and remove all other revision history versions.
- B. It will tag the device settings status as Auto-Update.
- C. It win install configuration changes to managed device automatically.
- D. It will modify the device-level database.
Answer: D
Explanation:
* Option C: It will modify the device-level database.This is correct. Reverting to a previous revision version in the revision history affects the device-level database by restoring it to the state saved in the selected revision. This ensures that any changes made after the selected revision are discarded, and the device configuration is returned to the earlier state.
Explanation of Incorrect Options:
* Option A: It will install configuration changes to managed devices automaticallyis incorrect because reverting a revision does not automatically push changes to the devices; it merely reverts the configuration on the FortiManager.
* Option B: It will tag the device settings status as Auto-Updateis incorrect because "Auto-Update" is not a status related to the revision history mechanism.
* Option D: It will generate a new version ID and remove all other revision history versionsis incorrect as reverting to a previous revision does not delete all other versions; it creates a new revision point for tracking.
FortiManager References:
* Refer to the "Revision Management" section in the FortiManager Administration Guide, which provides an overview of how revisions are managed and utilized for restoring configurations.
NEW QUESTION # 15
Refer to the exhibit.
What percent of the available RAM is being used by the process in charge of downloading the web and email filter databases from the public FortiGuard servers?
- A. 2.9
- B. 1.5
- C. 4.1
- D. 3.1
Answer: A
Explanation:
In the exhibit, the FortiManager CLI output displays the results of thetopcommand, which shows system processes, CPU usage, and memory (RAM) usage. We are specifically looking for the process responsible for downloading theweb and email filter databasesfrom the public FortiGuard servers. This process is typically handled by thefgdlinkdprocess.
Key information from the output:
* Thefgdlinkdprocess is listed with aPID of 1463.
* The%MEMcolumn shows that this process is using2.9%of the available RAM.
Evaluation of Options:
* A. 2.9: This iscorrect. Thefgdlinkdprocess, which handles the web and email filter database downloads, is using2.9%of the available memory, as indicated in the%MEMcolumn.
* B. 3.1: This is incorrect. The3.1%memory usage belongs to thefwmsvrdprocess, not the fgdlinkd process.
* C. 1.5: This is incorrect. The1.5%memory usage belongs to thefclinkdprocess, not the fgdlinkd process.
* D. 4.1: This is incorrect. The4.1%memory usage belongs to thefgdsvrprocess, not the fgdlinkd process.
NEW QUESTION # 16
Refer to the exhibit.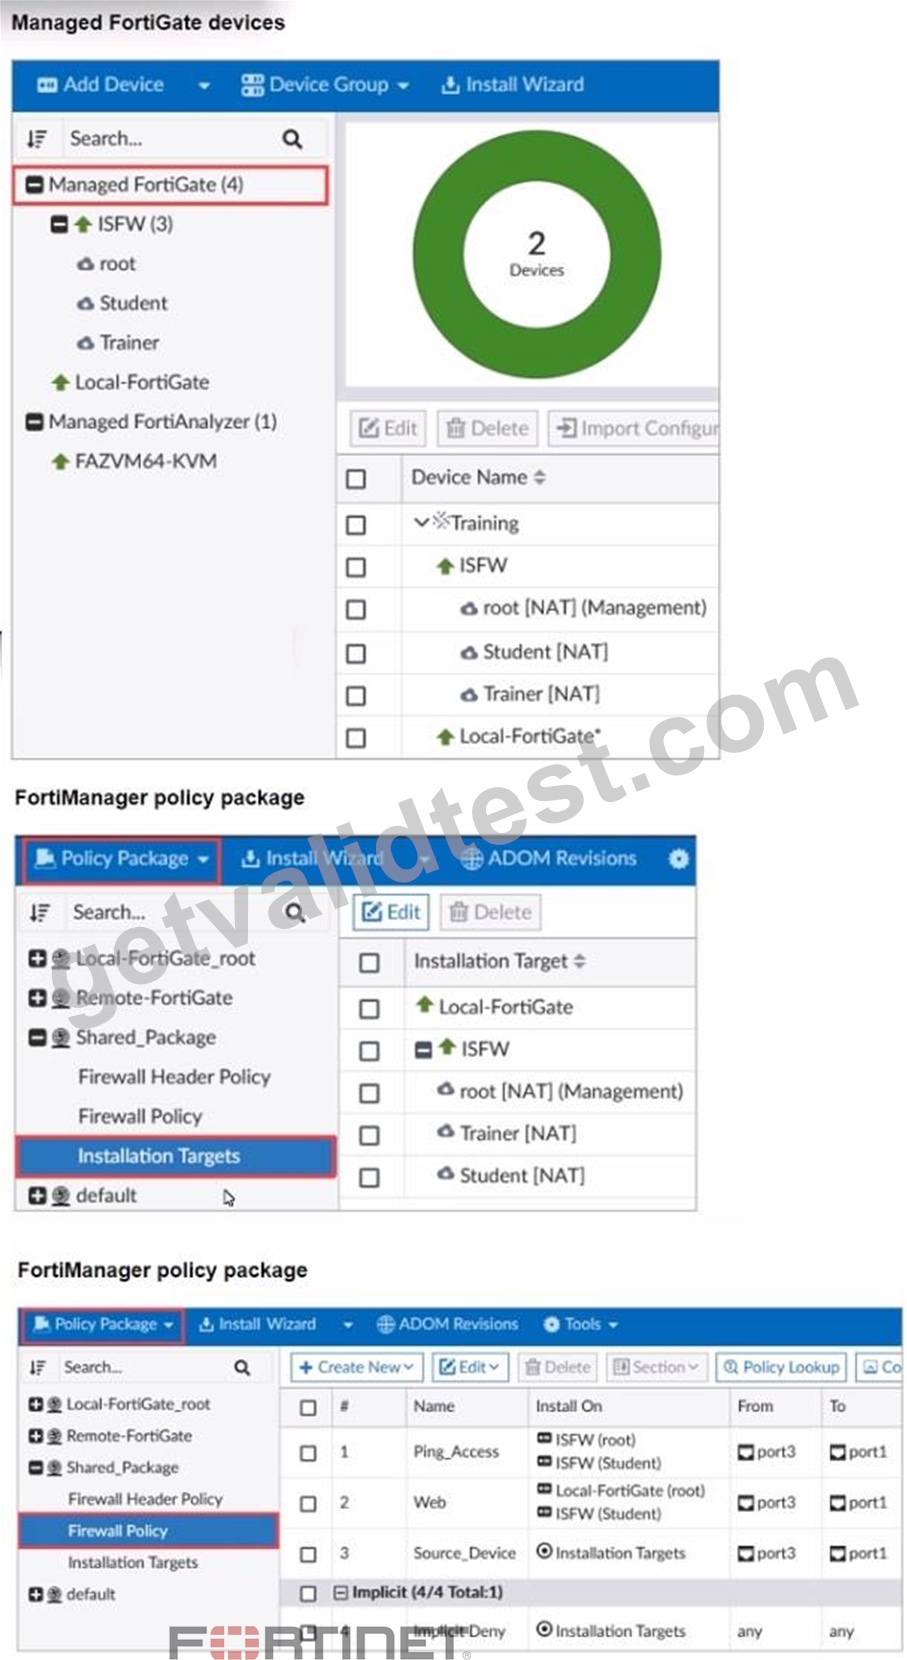
Given the configuration shown in the exhibit, which two conclusions can you draw from the installation targets in the Install On column? (Choose two.)
- A. Policy seq.# 1 will be installed on the ISFW device root[NAT] and Student[NAT] VDOMs only.
- B. Policy seq.# 2 will not be installed on the Local-FortiGate root VDOM because there is no root VDOM in the Installation Target
- C. Policy seq.# 3 will be skipped because no installation targets are specified.
- D. Policy seq.S will be installed on all managed devices and VDOMs that are listed under Installation Targets
Answer: A,D
Explanation:
* Option A: Policy seq.S will be installed on all managed devices and VDOMs that are listed under Installation Targets.This is correct. The "Install On" column indicates that the policy is targeted for installation on all listed managed devices and VDOMs under Installation Targets.
* Option D: Policy seq.# 1 will be installed on the ISFW device root[NAT] and Student[NAT] VDOMs only.This is correct. Policy sequence #1 specifies that it will be installed only on the ISFW device and the VDOMs 'root[NAT]' and 'Student[NAT]' as indicated by the "Install On" column.
Explanation of Incorrect Options:
* Option B: Policy seq.# 3 will be skipped because no installation targets are specifiedis incorrect because it is clearly listed under "Installation Targets," which means it will be installed according to the specified configuration.
* Option C: Policy seq.# 2 will not be installed on the Local-FortiGate root VDOM because there is no root VDOM in the Installation Targetis incorrect as the exhibit does not show any specific exclusion for seq.# 2 on the Local-FortiGate root VDOM.
FortiManager References:
* Refer to the FortiManager Administration Guide sections on "Policy Packages" and "Policy Installation Targets" for more details.
NEW QUESTION # 17
What is the purpose of ADOM revisions?
- A. To save the current state of all policy packages and objects for an ADOM
- B. To revert individual policy packages and device-level settings for a managed FortiGate
- C. To save the current state of the whole ADOM
- D. To save the FortiManager configuration in the System Checkpoints
Answer: A
Explanation:
* Option B: To save the current state of all policy packages and objects for an ADOMis the correct answer. ADOM (Administrative Domain) revisions in FortiManager are used to create a snapshot of the current state of all policy packages and objects associated with an ADOM. This allows administrators to save a specific configuration state and revert to it if necessary. It helps in managing changes and recovering from configuration errors or unintended changes.
* Explanation of Incorrect Options:
* Option A: To save the current state of the whole ADOMis incorrect because ADOM revisions specifically save only the policy packages and object configurations, not the entire state of the ADOM, which may include logs, reports, and other non-policy data.
* Option C: To revert individual policy packages and device-level settings for a managed FortiGateis incorrect as ADOM revisions are not meant for reverting individual policy packages or device settings; they are designed to handle the entire set of policy packages and objects within an ADOM.
* Option D: To save the FortiManager configuration in the System Checkpointsis incorrect because ADOM revisions do not function as system checkpoints for FortiManager itself; they are specific to ADOM policy packages and objects.
FortiManager References:
* Refer to the FortiManager 7.4 Administration Guide, "ADOM Management" section, which describes the purpose and usage of ADOM revisions for configuration management and restoration.
NEW QUESTION # 18
An administrator is in the process of copying a system template profile between ADOMs by runningthe following command: executefmprofile import-profile ADOM2 3547 /tmp/myfile Where does this command import the system template profile from?
- A. ADOM2 object database
- B. ADOM2 device database
- C. FortiManager file system
- D. Source ADOM policy database
Answer: C
NEW QUESTION # 19
Exhibit.
An administrator would like to create three ADOMs on FortiManager with different access levels based on departments. What two conclusions can you draw from the design shown in the exhibit? (Choose two.)
- A. The FortiManager administrator must set the ADOM device mode to Advanced
- B. An administrator with the super user profile can access all theVDOMs.
- C. The administrator must configure FortiManager in workspace normal mode.
- D. Policies and objects databases can be shared between the Financial and HR ADOMs.
Answer: A,B
NEW QUESTION # 20
An administrator is in the process of copying a system template profile between ADOMs by running the following command: execute fmprofile import-profile ADOM2 3547 /tmp/myfile Where does this command import the system template profile from?
- A. ADOM2 object database
- B. ADOM2 device database
- C. FortiManager file system
- D. Source ADOM policy database
Answer: C
Explanation:
The commandexecute fmprofile import-profile ADOM2 3547 /tmp/myfileis used to import a system template profile from the FortiManager file system. The path/tmp/myfileindicates a location in the FortiManager's local file system, from which the profile will be imported into the specified ADOM.
Options B, C, and D are incorrect because:
* B, C, and Dsuggest importing from different databases, which is not accurate since the command explicitly refers to the file system location.
FortiManager References:
* Refer to FortiManager 7.4 CLI Reference Guide: Commands for Profile Management.
NEW QUESTION # 21
Push updates are failing on a FortiGate device thatis located behind a NAT device. Which two settings should the administrator check? (Choose two.)
- A. That the override server IP address is set on FortiManager and the NAT device
- B. That the virtual IP address and correct ports are set on the NAT device
- C. That the NAT device IP address and correct ports are configured on FortiManager
- D. That the external IP address on the NAT device is set to DHCP and configured with the virtual IP
Answer: B,C
NEW QUESTION # 22
Which output is displayed right after moving the ISFW device from one ADOM to another?
- A.

- B.
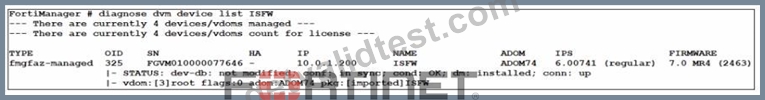
- C.

- D.

Answer: C
Explanation:
When a FortiGate device, like the ISFW (Internal Segmentation Firewall), is moved from one ADOM to another in FortiManager, the status of the device in the new ADOM will temporarily show some level of inconsistency or unknown state until the ADOM fully syncs and integrates the device.
In the provided options, we are analyzing the FortiManager diagnose dvm device list output for the ISFW device.
Explanation of the Outputs:
* Option A:
* The output shows that the device has the following status:
* dev-db: not modified
* conf: in sync
* cond: OK
* dm: retrieved
* The key part here is the pkg: [unknown]. This suggests that the configuration package for the ADOM in the new environment is still in anunknown state, which happens right after moving the device to a new ADOM. FortiManager needs time to process the device's configuration before syncing it properly.
* Option B:
* This output shows thepkg: [out-of-sync]. This occursaftersome configuration mismatch is identified, but it is not the immediate output after moving a device to a new ADOM.
* Option C:
* This output showspkg: [never-installed], which indicates that no package was ever installed on the device. This status typically appears when a device is newly added to FortiManager but not immediately after moving it between ADOMs.
* Option D:
* This output showspkg: [imported], which indicates that the device configuration has been successfully imported into the new ADOM. This would occur after the device is fully synced, but not immediately after moving the device to a new ADOM.
Conclusion:
The output that is displayedimmediately after movingthe ISFW device from one ADOM to another isOption A, where the package status is still unknown (pkg: [unknown]) because FortiManager has not yet fully synchronized the device's configuration in the new ADOM.
NEW QUESTION # 23
Which two items does an FGFM keepalive message include? (Choose two.)
- A. FortiGate IPS version
- B. FortiGate uptime
- C. FortiGate license information
- D. FortiGate configuration checksum
Answer: B,D
Explanation:
The FortiGate-FortiManager (FGFM) protocol is used for communication between a FortiGate device and FortiManager. Thekeepalive messagesare essential for maintaining communication and monitoring the health of the FortiGate devices connected to FortiManager. These messages provide important status information about the device.
Here are the items included in an FGFM keepalive message:
* A. FortiGate IPS version
* This isfalse. The IPS (Intrusion Prevention System) version is not included in the keepalive message. While IPS information can be part of other system syncs or monitoring processes, it is not part of the FGFM keepalive message.
* B. FortiGate license information
* This isfalse. The license information is not typically sent in the keepalive message. Licensing is checked and managed separately through other system operations and licensing checks.
* C. FortiGate configuration checksum
* This istrue. The configuration checksum is a critical part of the keepalive message, as it ensures that the configuration on the FortiGate matches the one managed by FortiManager. Any discrepancy would alert FortiManager to potential out-of-sync configurations.
* D. FortiGate uptime
* This istrue. The keepalive message includes the FortiGate's uptime, which allows FortiManager to track the health and stability of the connected FortiGate device.
NEW QUESTION # 24
An administrator has assigned a global policy package to custom ADOM1. Then the administrator creates a new policy package. Fortinet. in the custom ADOM1. What happens to the Fortinet policy package when it is created?
- A. The global policy package is automatically assigned.
- B. You must reapply the global policy package to ADOM1.
- C. You must assign the global policy package from the global ADOM.
- D. You can select the option to assign the global policies.
Answer: A
NEW QUESTION # 25
Which API method is used to create objects or overwrite existing ones?
- A. Set
- B. Add
- C. Update
- D. Exec
Answer: A
Explanation:
In the context of the FortiManager JSON API, thesetmethod is used tocreate new objectsoroverwrite existing ones. The API allows administrators to manage FortiManager and its associated devices by automating tasks like configuration changes, policy updates, and object creation.
Explanation of Options:
* A. Set:
* This istrue. Thesetmethod is used to create a new object if it does not exist or overwrite an existing object if it already exists. This method is frequently used in API requests to configure settings and apply changes on FortiManager.
* B. Add:
* This isfalse. Theaddmethod is used to add new objects without overwriting any existing ones. It is used when you want to create a new entry and ensure it doesn't conflict with or replace an existing object.
* C. Exec:
* This isfalse. Theexecmethod is used to execute specific actions or commands, rather than creating or modifying objects. This is typically used for actions like running scripts or executing operational commands on FortiManager or FortiGate.
* D. Update:
* This isfalse. While "update" might seem relevant, FortiManager's API does not specifically use an "update" method for modifying or creating objects. Thesetmethod serves that function by both creating new objects and overwriting existing ones.
NEW QUESTION # 26
In the event that one of the secondary FortiManager devices fails, which action must be performed to return the FortiManager HA manual mode to a working state?
- A. Reconfigure the primary device to remove the peer IP of the failed device.
- B. Manually promote one of the working secondary devices to the primary role, and reboot the old primary device to remove the peer IP of the failed device.
- C. The FortiManager HA state transition is transparent to administrators and does not require any reconfiguration.
- D. Reboot the failed device to remove its IP from the primary device.
Answer: A
NEW QUESTION # 27
An administrator enabled workspace mode and now wants to delete an address object that is currently referenced in a firewall policy. Which two results can the administrator expect? (Choose two.)
- A. FortiManager will disable the status of the address object until the changes are installed.
- B. FortiManager will not allow the administrator to delete a referenced address object until they lock the ADOM.
- C. FortiManager will temporarily change the status of the referenced firewall policy to disabled.
- D. FortiManager will replace the deleted address object with the none address object in the referenced firewall policy.
Answer: B,D
Explanation:
When operating in workspace mode on FortiManager 7.4, the administrator must understand how object references and deletions work:
* Option C- "FortiManager will not allow the administrator to delete a referenced address object until they lock the ADOM":In workspace mode, all changes are managed within an Administrative Domain (ADOM) scope. When an object (like an address object) is referenced in a policy, FortiManager prevents its deletion to maintain configuration integrity. The ADOM must be locked by the administrator to make changes to any referenced objects. This locking mechanism ensures that no unintended deletions or changes occur that could disrupt the policies or configuration.
* FortiManager Reference: "In workspace mode, changes to objects or policies require the ADOM to be locked. If an object is referenced, you must lock the ADOM before deleting or modifying the object." (FortiManager 7.4 Administration Guide, Section on Workspace Mode and ADOM Management)
* Option D- "FortiManager will replace the deleted address object with the none address object in the referenced firewall policy":If the administrator attempts to delete an address object that is currently referenced by a firewall policy, FortiManager will replace the deleted object with the 'none' address object. This is done to maintain the policy structure and avoid policy corruption due to a missing reference. This behavior ensures that the firewall policy remains syntactically correct, even though the specific address object is no longer in use.
* FortiManager Reference: "When a referenced object is deleted, FortiManager will replace it with a 'none' object in the policy. This behavior is to ensure the integrity and continuity of the policy configurations." (FortiManager 7.4 Administration Guide, Object Management and Policy Handling in Workspace Mode)
NEW QUESTION # 28
Refer to the exhibit which shows the Download Import Report.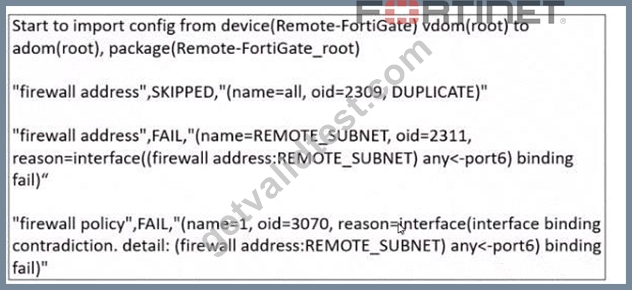
Why is FortiManager failing to import firewall policy ID 1?
- A. Policy ID 1 for this managed FortiGate already exists on FortiManager in the policy package named Remote-FortlGate.
- B. Policy ID 1 is configured from the interface any to port6. FortiManager rejects the request to import this policy because the any interface does not exist on FortiManager
- C. Policy ID 1 has an address object that already exists in the ADOM database with any as the interface association, and conflicts with the address object interface association locally on FortiGate.
- D. Policy ID 1 does not have the ADOM Interface mapping configured on FortiManager.
Answer: A
NEW QUESTION # 29
......
Verified FCP_FMG_AD-7.4 dumps Q&As - 2024 Latest FCP_FMG_AD-7.4 Download: https://www.getvalidtest.com/FCP_FMG_AD-7.4-exam.html
Dumps Questions [2024] Pass for FCP_FMG_AD-7.4 Exam: https://drive.google.com/open?id=1k9TkmdoG_TScdj3_ORIf_FBCR1x-DL_j