


[Dec-2025] Get 100% Real HPE7-A02 Exam Questions, Accurate & Verified GetValidTest Dumps in the Real Exam!
Pass Your HP ACNSP Exams Fast. All Top HPE7-A02 Exam Questions Are Covered.
Achieving the HP HPE7-A02 certification is a great way to enhance your career prospects as a network security professional. Aruba Certified Network Security Professional Exam certification demonstrates to employers and clients that you have the skills and knowledge required to design, implement, and manage secure wireless networks using Aruba products. Additionally, the certification provides a solid foundation for further career advancement and specialization within the field of network security.
HPE7-A02 exam focuses on topics such as Aruba security solutions, firewall technologies, VPN technologies, and network access control. HPE7-A02 exam also covers advanced topics such as threat management and mitigation, wireless intrusion prevention, and secure network design. Aruba Certified Network Security Professional Exam certification is suitable for professionals who work in a variety of roles such as network security engineers, network administrators, and network consultants. By earning the Aruba Certified Network Security Professional certification, individuals can demonstrate their expertise in network security and enhance their career opportunities.
NEW QUESTION # 26
A company needs you to integrate HPE Aruba Networking ClearPass Policy Manager (CPPM) with HPE Aruba Networking ClearPass Device Insight (CPDI).
What is one task you should do to prepare?
- A. Install the root CA for CPPM's HTTPS certificate as trusted in the CPDI application.
- B. Configure WMI, SSH, and SNMP external accounts for device scanning on CPPM.
- C. Enable Insight in the CPPM server configuration settings.
- D. Collect a Data Collector token from HPE Aruba Networking Central.
Answer: C
Explanation:
To integrate HPE Aruba Networking ClearPass Policy Manager (CPPM) with HPE Aruba Networking ClearPass Device Insight (CPDI), one of the necessary tasks is to enable Insight in the CPPM server configuration settings. This configuration allows CPPM to communicate and share data with CPDI, facilitating the integration and enabling enhanced device profiling and policy enforcement capabilities.
1.Insight Enablement: Enabling Insight on the CPPM server allows it to leverage the data and capabilities of CPDI, integrating device profiling information into policy decisions.
2.Data Sharing: This integration ensures that CPPM can receive and use detailed device information from CPDI to make more informed policy enforcement decisions.
3.Configuration: Properly configuring the server settings to enable Insight ensures seamless communication and data flow between CPPM and CPDI.
NEW QUESTION # 27
Assume that an AOS-CX switch is already implementing DHCP snooping and ARP inspection successfully on several VLANs.
What should you do to help minimize disruption time if the switch reboots?
- A. Configure the switch to act as an ARP proxy.
- B. Save the IP-to-MAC bindings to external storage.
- C. Create static IP-to-MAC bindings for the DHCP and DNS servers.
- D. Configure the IP helper address on this switch, rather than a core routing switch.
Answer: B
Explanation:
To minimize disruption time if an AOS-CX switch reboots while implementing DHCP snooping and ARP inspection, you should save the IP-to-MAC bindings to external storage. This ensures that the DHCP snooping and ARP inspection tables, which are crucial for preventing spoofing attacks, are preserved across reboots. When the switch restarts, it can reload these bindings from the external storage, thereby maintaining network security and reducing the downtime associated with rebuilding these tables.
1.Preserving Bindings: Saving IP-to-MAC bindings to external storage ensures that these critical security tables are not lost during a reboot, maintaining network integrity.
2.Security Continuity: This practice helps to quickly restore security features like DHCP snooping and ARP inspection, minimizing the window of vulnerability.
3.Operational Efficiency: By preserving these bindings, the switch can resume normal operations faster, reducing disruption to network services.
NEW QUESTION # 28
A company has HPE Aruba Networking APs running AOS-10 and managed by HPE Aruba Networking Central. The company also has AOS-CX switches. The security team wants you to capture traffic from a particular wireless client. You should capture this client's traffic over a 15-minute time period and then send the traffic to them in a PCAP file. What should you do?
- A. Access the CLI for the client's AP. Set up a mirroring session between its radio and a management station running Wireshark.
- B. Go to that client in HPE Aruba Networking Central. Use the "Live Events" page to run a packet capture.
- C. Access the CLI for the client's AP's switch. Set up a mirroring session between the AP's port and a management station running Wireshark.
- D. Go to the client's AP in HPE Aruba Networking Central. Use the "Security" page to run a packet capture.
Answer: D
Explanation:
* Packet Capture in Aruba Central:
* Aruba Central provides tools for remote packet captures directly from the APs.
* On the "Security" page for the AP, you can initiate a packet capture session, specifying the client device and capture duration.
* The traffic is captured into a PCAP file, which can be downloaded and analyzed using tools like Wireshark.
* Option Analysis:
* Option A: Incorrect. While possible via CLI, Aruba Central provides a simpler method for packet captures.
* Option B: Correct. Aruba Central's "Security" page allows you to capture and export client traffic efficiently.
* Option C: Incorrect. The "Live Events" page focuses on monitoring events, not packet captures.
* Option D: Incorrect. Port mirroring on the switch captures AP traffic but requires more manual configuration and does not isolate client-specific wireless traffic easily.
NEW QUESTION # 29
Refer to Exhibit.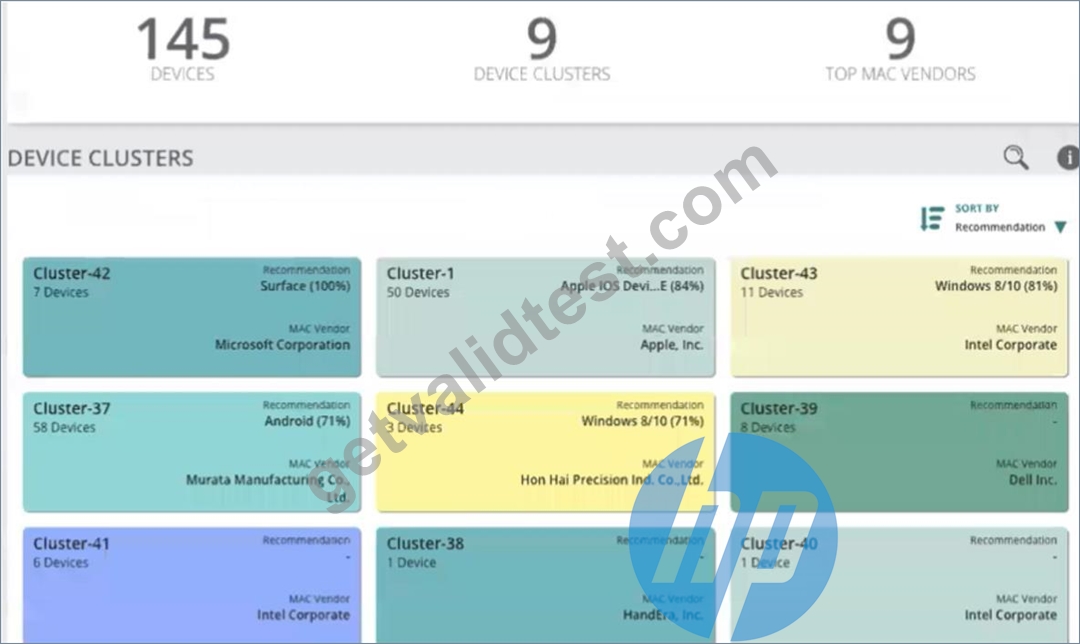
A company is using HPE Aruba Networking ClearPass Device Insight (CPDI) (the standalone application).
In the CPDI interface, you go to the Generic Devices
page and see the view shown in the exhibit.
What correctly describes what you see?
- A. Each cluster is a group of unclassified devices that CPDI's machine learning has discovered to have similar attributes.
- B. Each cluster is all the devices that have been assigned to the same category by one of CPDI's built-in system rules.
- C. Each cluster is a group of devices that match one of the tags configured by admins.
- D. Each cluster is a group of devices that have been classified with user rules, but for which CPDI offers different recommendations.
Answer: A
Explanation:
In HPE Aruba Networking ClearPass Device Insight (CPDI), the clusters shown in the exhibit represent groups of unclassified devices that CPDI's machine learning algorithms have identified as having similar attributes. These clusters are formed based on observed characteristics and behaviors of the devices, helping administrators to categorize and manage devices more effectively.
1.Machine Learning: CPDI uses machine learning to analyze device attributes and group them into clusters based on similarities.
2.Unclassified Devices: These clusters typically represent devices that have not yet been explicitly classified by admins but share common attributes that suggest they belong to the same category.
3.Management: This clustering helps in simplifying the process of managing and applying policies to groups of similar devices.
NEW QUESTION # 30
A company wants to use the HPE Aruba Networking ClearPass OnGuard agent to assign posture to clients.
How do you define the conditions by which a client receives a particular posture?
- A. Create rules directly in a service's Posture tab
- B. Create the rules directly in a service's Enforcement tab
- C. Create rules within a WebAuth enforcement policy
- D. Create rules within a posture policy
Answer: D
Explanation:
ClearPass OnGuard uses a Posture Policy object to define:
* Which checks are performed (e.g., AV installed, firewall status, patches)
* How the results map to posture tokens such as "Healthy," "Quarantined," etc.
The official OnGuard configuration workflow states that you must first "Define the posture policy", and that these posture policies contain the rules for evaluating health and determining posture tokens.
Service enforcement policies then consume the posture token (e.g., Tips:Posture = Healthy) but do not define the posture conditions themselves. The "Posture" tab on a service is used to enable posture and associate it with the posture policy; the detailed rules live in the posture policy object.
Therefore, posture logic is defined by creating rules within a posture policy # Option A.
NEW QUESTION # 31
You have created this rule in an HPE Aruba Networking ClearPass Policy Manager (CPPM) service's enforcement policy: IF Authorization [Endpoints Repository] Conflict EQUALS true THEN apply "quarantine_profile" What information can help you determine whether you need to configure cluster-wide profiler parameters to ignore some conflicts?
- A. Whether the company has devices that use PXE boot
- B. Whether the company has rare Internet of Things (loT) devices
- C. Whether some devices are running legacy operating systems
- D. Whether some devices are incapable of captive portal or 802.1X authentication
Answer: A
Explanation:
When you have created a rule in a ClearPass Policy Manager (CPPM) service's enforcement policy to quarantine devices with endpoint conflicts, it is important to consider whether the company has devices that use PXE boot. PXE booting devices can create conflicts in the profiler because they may temporarily have different network attributes (e.g., MAC address or IP address) before fully booting and obtaining their final configuration. Understanding whether PXE boot is in use can help determine if profiler parameters need to be adjusted to ignore such temporary conflicts, ensuring that devices are not incorrectly quarantined.
Reference: ClearPass profiler configuration documentation and best practices include considerations for handling network devices with dynamic or temporary configurations, such as those using PXE boot.
NEW QUESTION # 32
A company wants you to create a custom device fingerprint on CPPM with rules for profiling a group of specialized devices. What is one requirement?
- A. Enabling HPE Aruba Networking ClearPass Device Insight integration with the correct Data Collector token.
- B. Disabling the "Automatically download Endpoint Profiler Fingerprints" feature in cluster-wide parameters.
- C. Pre-defining the desired attributes and rules in an XML format file.
- D. Connecting a known device of this type and getting it discovered in CPPM's Endpoints Repository.
Answer: D
Explanation:
* Custom Device Fingerprinting on CPPM:
* To create a custom fingerprint, you first need to connect a known device of that type to the network.
* CPPM will discover the device in its Endpoints Repository, allowing you to analyze its attributes (e.g., MAC OUI, DHCP options) and create custom profiling rules.
* Option Analysis:
* Option A: Correct. Discovering a known device in the Endpoints Repository is a prerequisite for creating accurate custom fingerprint rules.
* Option B: Incorrect. CPDI integration is not required for custom fingerprints on CPPM.
* Option C: Incorrect. XML rules are not pre-defined; they are created dynamically based on observed attributes.
* Option D: Incorrect. The "Automatically download Endpoint Profiler Fingerprints" setting is unrelated to custom profiling.
NEW QUESTION # 33
What is one benefit of integrating HPE Aruba Networking ClearPass Policy Manager (CPPM) with third-party solutions such as Mobility Device Management (MDM) and firewalls?
- A. CPPM can make the third-party solutions more secure by adding signature-based threat detection capabilities.
- B. CPPM can exchange contextual information about clients with third-party solutions, which helps make better decisions.
- C. CPPM can offload policy decisions to the third-party solutions, enabling CPPM to respond to authentication requests more quickly.
- D. CPPM can take over filtering internal traffic so that the third-party solutions have more processing power to devote to filtering external traffic.
Answer: B
Explanation:
* Contextual Exchange for Better Decisions:
* HPE Aruba ClearPass can integrate with third-party solutions like MDM and firewalls to exchange contextual information about endpoints (e.g., device type, posture, location).
* This integration allows ClearPass and the third-party solutions to make better access control and security decisions.
* For example:
* An MDM can inform CPPM about device compliance, and CPPM can adjust enforcement policies dynamically.
* Firewalls can receive updated context about users and devices to enforce policies more effectively.
* Option Analysis:
* Option A: Correct. Exchanging contextual information improves access control decisions.
* Option B: Incorrect. CPPM does not provide signature-based threat detection.
* Option C: Incorrect. CPPM does not offload policy decisions; it integrates for collaboration.
* Option D: Incorrect. CPPM does not replace third-party traffic filtering capabilities.
NEW QUESTION # 34 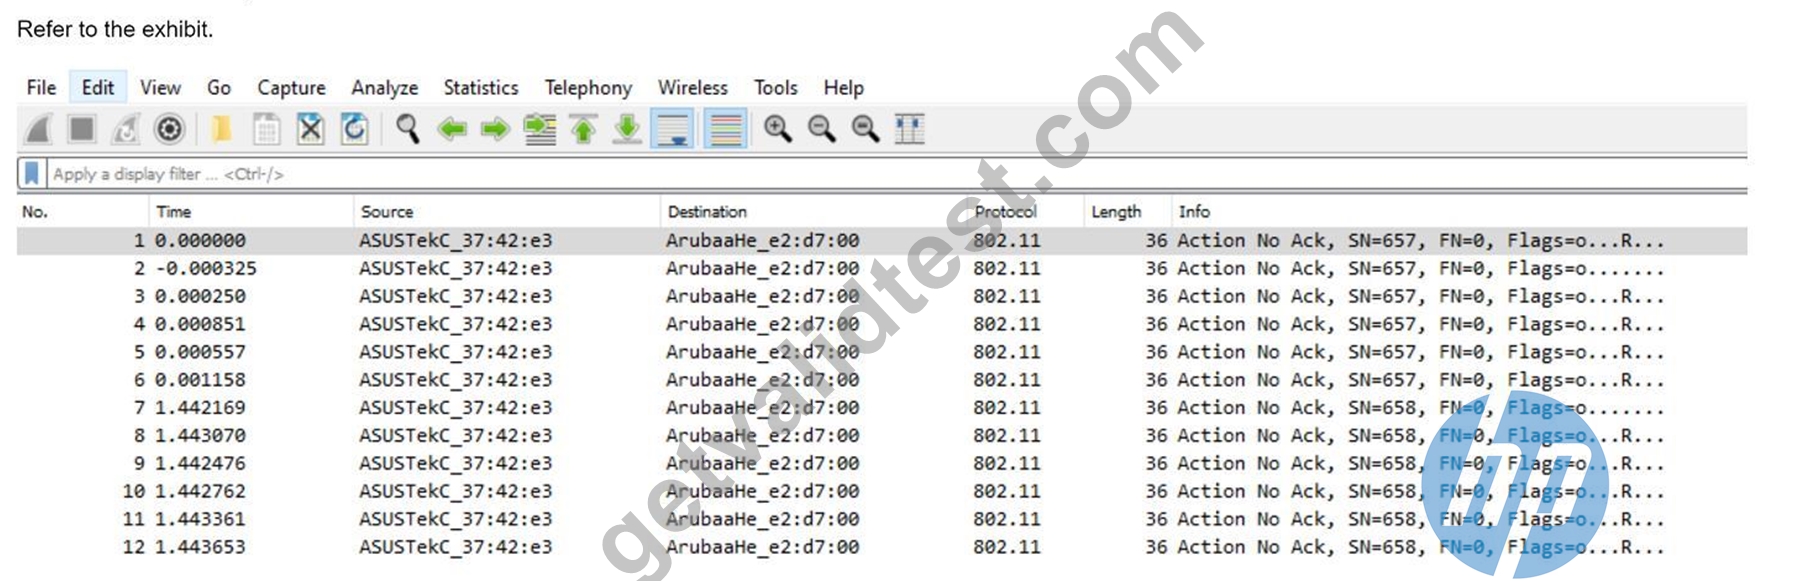
You have downloaded a packet capture that you generated on HPE Aruba Networking Central. When you open the capture in Wireshark, you see the output shown in the exhibit.
What should you do in Wireshark so that you can better interpret the packets?
- A. Edit preferences for IEEE 802.11 and chose to ignore the Protection bit with IV.
- B. Apply the following display filter: wlan.fc.type == 1.
- C. Edit the Enabled Protocols and make sure that 802.11, GRE, and Aruba_ERM are enabled.
- D. Choose to decode UDP port 5555 packets as ARUBA_ERM and set the Aruba ERM Type to 0.
Answer: D
Explanation:
To better interpret the packets shown in the Wireshark capture, you should choose to decode UDP port 5555 packets as ARUBA_ERM and set the Aruba ERM Type to 0. This configuration will allow Wireshark to properly decode and display the Aruba-specific encapsulated remote mirroring (ERM) packets, providing a clearer understanding of the traffic.
1.Decoding Protocols: Selecting the correct protocol decoding in Wireshark ensures that the captured packets are interpreted correctly, displaying the relevant information.
2.Aruba ERM: The packets in the capture are likely encapsulated remote mirroring (ERM) packets specific to Aruba, which require proper decoding settings in Wireshark.
3.Clear Interpretation: By setting the Aruba ERM Type to 0 and decoding the packets as ARUBA_ERM, you can view the encapsulated data accurately.
NEW QUESTION # 35
You are setting up an HPE Aruba Networking VIA solution for a company. You need to configure access control policies for applications and resources that remote clients can access when connected to the VPN.
Where on the VPNC should you configure these policies?
- A. In the tunneled network settings within the VIA Connection Profile
- B. In the roles to which VIA clients are assigned after VIA Web authentication
- C. In the cloud security settings using IPsec maps
- D. In the roles to which VIA clients are assigned after IKE authentication
Answer: D
Explanation:
To configure access control policies for applications and resources that remote clients can access when connected to the VPN, you should configure these policies in the roles to which VIA clients are assigned after IKE (Internet Key Exchange) authentication on the VPNC. These roles define the permissions and access controls for the clients once they are authenticated, ensuring that they can only access the applications and resources allowed by their assigned roles.
1.IKE Authentication: After IKE authentication, clients are assigned specific roles that determine their access privileges.
2.Role-Based Access Control: By configuring access control policies within these roles, you can granularly control what resources and applications the remote clients can access over the VPN.
3.Security: This method ensures that access is managed securely and dynamically based on the role assigned to each client after successful authentication.
Reference: Aruba's VPN and VIA deployment guides provide detailed instructions on configuring roles and access control policies for remote VPN clients.
NEW QUESTION # 36
You have configured an AOS-CX switch to implement 802.1X on edge ports. Assume ports operate in the default auth-mode. VolP phones are assigned to the
"voice" role and need to send traffic that is tagged for VLAN 12.
Where should you configure VLAN 12?
- A. As the trunk native VLAN on edge ports and the trunk native VLAN on the "voice" role
- B. As the allowed trunk VLAN in the "voice" role (and not in the edge port settings)
- C. As the trunk native VLAN in the "voice" role (and not in the edge port settings)
- D. As a trunk allowed VLAN on edge ports and the trunk native VLAN in the "voice" role
Answer: B
Explanation:
When configuring 802.1X authentication on edge ports of an AOS-CX switch and assigning VoIP phones to a
"voice" role, the correct approach is to configure VLAN 12 as the allowed trunk VLAN in the "voice" role.
This setup ensures that traffic tagged for VLAN 12 is appropriately managed by the role applied to the VoIP phones. In AOS-CX switches, the role-based VLAN configuration allows for more granular control and ensures that the VoIP phones' traffic is handled correctly without altering the edge port settings, which typically operate with default settings for authentication.
NEW QUESTION # 37
What is one use case that companies can fulfill using HPE Aruba Networking ClearPass Policy Manager's (CPPM's) Device Profiler?
- A. OIdentifying device security vulnerabilities by CVE ID and receiving remediation recommendations
- B. Assigning different AOS firewall roles to users on computers and the same users on smartphones
- C. Leveraging artificial intelligence to more accurately identify Internet of Things (loT) devices
- D. Quarantining devices that do not have the required antivirus software installed on them
Answer: C
Explanation:
One use case that companies can fulfill using HPE Aruba Networking ClearPass Policy Manager's (CPPM's) Device Profiler is leveraging artificial intelligence to more accurately identify Internet of Things (IoT) devices. ClearPass Device Profiler uses AI and machine learning to analyze network traffic and device behavior, providing detailed and accurate identification of IoT devices on the network. This helps in managing and securing diverse and numerous IoT devices by ensuring they are correctly profiled and assigned appropriate access policies.
Reference: Aruba ClearPass documentation highlights the use of AI and machine learning in device profiling to enhance the identification and management of IoT devices.
NEW QUESTION # 38
What is one use case that companies can fulfill using HPE Aruba Networking ClearPass Policy Manager's (CPPM's) Device Profiler?
- A. Quarantining and remediating devices that have disabled firewalls
- B. Authenticating clients to Active Directory computer accounts
- C. Applying the correct enforcement profiles to specialized clients such as security cameras
- D. Identifying OS, browser, and application vulnerabilities by CVE ID
Answer: C
Explanation:
ClearPass Device Profiler gathers information (DHCP, HTTP user-agent, MAC OUI, RADIUS, etc.) to identify device types and roles-especially non-user devices. Aruba documentation describes using profiling to recognize and categorize devices such as IP cameras, printers, and IoT "bots", and to supply this identity context to access control policies. ExamTopics Typical use cases include:
* Automatically identifying a device as a security camera, printer, IP phone, etc.
* Using that profile to assign an appropriate role/VLAN and enforcement profile in CPPM (e.g., restricted video-surveillance VLAN).
ClearPass literature explicitly calls out that Device Profiler is used to "automatically profile devices and provide an identity context (such as cameras, printers, or bots)" that can be used in policy decisions.
Options B, C, and D are handled by vulnerability scanners, directory services, or posture/OnGuard, not by Device Profiler itself. Therefore the correct use case is Option A.
NEW QUESTION # 39
You need to set up HPE Aruba Networking ClearPass Policy Manager (CPPM) to provide certificate- based authentication of 802.1X supplicants. How should you upload the root CA certificate for the supplicants' certificates?
- A. As a ClearPass Server certificate with the RADIUS/EAP usage.
- B. As a Trusted CA with the AD/LDAP usage.
- C. As a Trusted CA with the EAP usage.
- D. As a ClearPass Server certificate with the Database usage.
Answer: C
Explanation:
* 802.1X Authentication Workflow: Requires the root CA certificate of the issuing authority for the supplicants' certificates. This ensures that the server can validate the client certificate during the EAP- TLS handshake.
* Trusted CA Usage: In ClearPass, certificates with "Trusted CA" usage are used for validating client and server identities during secure authentication exchanges.
* Option A: Incorrect. The "ClearPass Server certificate" is used for server-side identity verification and is not used to validate client certificates.
* Option B: Incorrect. Database usage is unrelated to RADIUS/EAP or certificate validation.
* Option C: Incorrect. While LDAP/AD integration supports certificate validation, this is not the primary purpose of Trusted CAs for 802.1X.
* Option D: Correct. Trusted CAs for EAP are required to validate client certificates during the authentication process.
By uploading the root CA as a "Trusted CA with EAP usage," the CPPM can properly authenticate the certificates presented by the supplicants during EAP-TLS negotiations.
NEW QUESTION # 40
What is one use case that companies can fulfill using HPE Aruba Networking ClearPass Policy Manager's (CPPM's) Device Profiler?
- A. OIdentifying device security vulnerabilities by CVE ID and receiving remediation recommendations
- B. Assigning different AOS firewall roles to users on computers and the same users on smartphones
- C. Leveraging artificial intelligence to more accurately identify Internet of Things (loT) devices
- D. Quarantining devices that do not have the required antivirus software installed on them
Answer: C
Explanation:
One use case that companies can fulfill using HPE Aruba Networking ClearPass Policy Manager's (CPPM's) Device Profiler is leveraging artificial intelligence to more accurately identify Internet of Things (IoT) devices. ClearPass Device Profiler uses AI and machine learning to analyze network traffic and device behavior, providing detailed and accurate identification of IoT devices on thenetwork. This helps in managing and securing diverse and numerous IoT devices by ensuring they are correctly profiled and assigned appropriate access policies.
NEW QUESTION # 41
Your company wants to implement Tunneled EAP (TEAP).
How can you set up HPE Aruba Networking ClearPass Policy Manager (CPPM) to enforce certificated-based authentication for clients using TEAP?
- A. Create an authentication method named "TEAP" with the type set to EAP-TLS.
- B. For the service using TEAP, set the authentication source to an internal database.
- C. Select a service certificate when you specify TEAP as a service's authentication method.
- D. Select an EAP-TLS-type authentication method for the TEAP method's inner method.
Answer: D
Explanation:
To set up HPE Aruba Networking ClearPass Policy Manager (CPPM) to enforce certificate-based authentication for clients using Tunneled EAP (TEAP), you need to select an EAP-TLS-type authentication method for TEAP's inner method. TEAP allows for a combination of certificate-based (EAP-TLS) and password-based (EAP-MSCHAPv2) authentication. By choosing EAP-TLS as the inner method, you ensure that the clients are authenticated using their certificates, thus enforcing certificate-based authentication within the TEAP framework.
NEW QUESTION # 42
A company has Aruba APs that are controlled by Central and that implement WIDS. When you check WIDS events, you see a "detect valid SSID misuse" event. What can you interpret from this event, and what steps should you take?
- A. Clients are failing to authenticate to corporate SSIDs. You should first check for misconfigured authentication settings and then investigate a possible threat.
- B. Hackers are likely trying to pose as authorized APs. You should use the detecting radio information and immediately track down the device that triggered the event.
- C. Admins have likely misconfigured SSID security settings on some of the company's APs. You should have them check those settings.
- D. This event might be a threat but is almost always a false positive. You should wait to see the event over several days before following up on it.
Answer: B
Explanation:
The "Detect Valid SSID Misuse" event in Aruba's Wireless Intrusion Detection System (WIDS) indicates that a valid SSID, associated with your network, is being broadcast from an unauthorized source. This scenario often signals a potential rogue access point attempting to deceive clients into connecting to it (e.g., for credential harvesting or man-in-the-middle attacks).
1. Explanation of Each Option
A: Clients are failing to authenticate to corporate SSIDs. You should first check for misconfigured authentication settings and then investigate a possible threat:
* Incorrect:
* This event is not related to authentication failures by legitimate clients.
* Misconfigured authentication settings would lead to events like "authentication failures" or
"radius issues," not "valid SSID misuse."
B: Admins have likely misconfigured SSID security settings on some of the company's APs. You should have them check those settings:
* Incorrect:
* This event refers to an external device broadcasting your SSID, not misconfiguration on the company's authorized APs.
* WIDS differentiates between valid corporate APs and rogue APs.
C: Hackers are likely trying to pose as authorized APs. You should use the detecting radio information and immediately track down the device that triggered the event:
* Correct:
* This is the most likely cause of the "detect valid SSID misuse" event. A rogue AP broadcasting a corporate SSID could lure clients into connecting to it, exposing sensitive credentials or traffic.
* Immediate action includes:
* Using the radio information from the event logs to identify the rogue AP's location.
* Physically locating and removing the rogue device.
* Strengthening WIPS/WIDS policies to prevent further misuse.
D: This event might be a threat but is almost always a false positive. You should wait to see the event over several days before following up on it:
* Incorrect:
* While false positives are possible, "valid SSID misuse" is a critical security event that should not be ignored.
* Delaying action increases the risk of successful attacks against your network.
2. Recommended Steps to Address the Event
* Review Event Logs:
* Gather details about the rogue AP, such as SSID, MAC address, channel, and signal strength.
* Locate the Rogue Device:
* Use the detecting AP's radio information and signal strength to triangulate the rogue AP's physical location.
* Respond to the Threat:
* Remove or disable the rogue device.
* Notify the security team for further investigation.
* Prevent Future Misuse:
* Strengthen security policies, such as enabling client whitelists or enhancing WIPS protection.
References
* Aruba WIDS/WIPS Configuration and Best Practices Guide.
* Aruba Central Security Event Analysis Documentation.
* Wireless Threat Management Using Aruba Networks.
NEW QUESTION # 43
Your company wants to implement Tunneled EAP (TEAP).
How can you set up HPE Aruba Networking ClearPass Policy Manager (CPPM) to enforce certificated-based authentication for clients using TEAP?
- A. Create an authentication method named "TEAP" with the type set to EAP-TLS.
- B. For the service using TEAP, set the authentication source to an internal database.
- C. Select a service certificate when you specify TEAP as a service's authentication method.
- D. Select an EAP-TLS-type authentication method for the TEAP method's inner method.
Answer: D
Explanation:
To set up HPE Aruba Networking ClearPass Policy Manager (CPPM) to enforce certificate-based authentication for clients using Tunneled EAP (TEAP), you need to select an EAP-TLS-type authentication method for TEAP's inner method. TEAP allows for a combination of certificate-based (EAP-TLS) and password-based (EAP-MSCHAPv2) authentication. By choosing EAP-TLS as the inner method, you ensure that the clients are authenticated using their certificates, thus enforcing certificate-based authentication within the TEAP framework.
Reference: Aruba ClearPass documentation provides detailed steps for configuring TEAP and selecting appropriate inner authentication methods to ensure secure certificate-based client authentication.
NEW QUESTION # 44
A company uses HPE Aruba Networking ClearPass Policy Manager (CPPM) as a TACACS+ server to authenticate managers on its AOS-CX switches. You want to assign managers to groups on the AOS-CX switch by name.
How do you configure this setting in a CPPM TACACS+ enforcement profile?
- A. Add the Shell service and set autocmd to the group name.
- B. Add the Shell service and set priv-Ivl to the group name.
- C. Add the Aruba:Common service and set Aruba-Priv-Admin-User to the group name.
- D. Add the Aruba:Common service and set Aruba-Admin-Role to the group name.
Answer: D
Explanation:
To assign managers to groups on the AOS-CX switch by name using HPE Aruba Networking ClearPass Policy Manager (CPPM) as a TACACS+ server, you should add the Aruba service to the TACACS+ enforcement profile and set the Aruba-Admin-Role to the group name. This configuration ensures that the appropriate administrative roles are assigned to managers based on their group membership, allowing for role-based access control on the AOS-CX switches.
Reference: ClearPass TACACS+ configuration guides and AOS-CX switch management documentation provide details on setting up enforcement profiles and using the Aruba-Admin-Role attribute for role assignment.
NEW QUESTION # 45
HPE Aruba Networking Central displays an alert about an Infrastructure Attack that was detected. You go to the Security > RAPIDS events and see that the attack was "Detect adhoc using Valid SSID." What is one possible next step?
- A. Make sure that you have tuned the threshold for that check, as false positives are common for it.
- B. Look for the IP address associated with the offender and then check for that IP address among HPE Aruba Networking Central clients.
- C. Make sure that clients have updated drivers, as faulty drivers are a common explanation for this attack type.
- D. Use HPE Aruba Networking Central floorplans or the detecting AP identities to locate the general area for the threat.
Answer: D
Explanation:
When HPE Aruba Networking Central detects an Infrastructure Attack, such as "Detect adhoc using Valid SSID," the next step is to locate the general area of the threat. You can use HPE ArubaNetworking Central floorplans or the identities of the detecting APs to pinpoint the approximate location of the adhoc network.
This allows you to physically investigate and address the source of the threat, ensuring that unauthorized or rogue networks are quickly identified and mitigated.
NEW QUESTION # 46
A company needs you to integrate HPE Aruba Networking ClearPass Policy Manager (CPPM) with HPE Aruba Networking ClearPass Device Insight (CPDI).
What is one task you should do to prepare?
- A. Install the root CA for CPPM's HTTPS certificate as trusted in the CPDI application.
- B. Configure WMI, SSH, and SNMP external accounts for device scanning on CPPM.
- C. Enable Insight in the CPPM server configuration settings.
- D. Collect a Data Collector token from HPE Aruba Networking Central.
Answer: C
Explanation:
To integrate HPE Aruba Networking ClearPass Policy Manager (CPPM) with HPE Aruba Networking ClearPass Device Insight (CPDI), one of the necessary tasks is to enable Insight in the CPPM server configuration settings. This configuration allows CPPM to communicate and share data with CPDI, facilitating the integration and enabling enhanced device profiling and policy enforcement capabilities.
1.Insight Enablement: Enabling Insight on the CPPM server allows it to leverage the data and capabilities of CPDI, integrating device profiling information into policy decisions.
2.Data Sharing: This integration ensures that CPPM can receive and use detailed device information from CPDI to make more informed policy enforcement decisions.
3.Configuration: Properly configuring the server settings to enable Insight ensures seamless communication and data flow between CPPM and CPDI.
Reference: Aruba ClearPass integration guides provide detailed instructions on enabling Insight and configuring the necessary settings for effective integration between CPPM and CPDI.
NEW QUESTION # 47
......
Penetration testers simulate HPE7-A02 exam: https://www.getvalidtest.com/HPE7-A02-exam.html
Free Test Engine For Aruba Certified Network Security Professional Exam Certification Exams: https://drive.google.com/open?id=19XS3YOeAZrly2ZIfy1HeFOfpgN9mmo60