


Get instant access to C1000-018 Practice Tests 2021 Free Updated Today!
Welcome to download the newest PassLeader C1000-018 PDF dumps ( 62 Q&As)
NEW QUESTION 29
Which considering the ability to tune False Positives with the Confidence factor Setting, which statement applies?
- A. When setting a confidence factor, using a higher value will result in a higher number of Offenses.
- B. To ensure that the results are comparable, it is important to apply a common Confidence Factor across all network segments.
- C. Secure areas should have a lower confidence value, while less secure areas should have a higher confidence value.
- D. Secure areas should have a higher confidence value, while less secure areas should have a lower confidence value a higher,,
Answer: D
NEW QUESTION 30
What is the reason for this system notification?
"Time synchronization to primary or Console has failed"
- A. Deny ntpdate communication on port 223.
- B. Deny ntpdate communication on port 423.
- C. Deny ntpdate communication on port 323.
- D. Deny ntpdate communication on port 123
Answer: D
Explanation:
Explanation
https://www.ibm.com/docs/en/qradar-on-cloud?topic=appliances-time-synchronization-failed The managed host cannot synchronize with the console or the secondary HA appliance cannot synchronize with the primary appliance.
Administrators must allow ntpdate communication on port 123. When time synchronization is incorrect, data might not be reported correctly to the console. The longer the systems go without synchronization, the higher the risk that a search for data, report, or offense might return an incorrect result. Time synchronization is critical to successful requests from managed host and appliances
NEW QUESTION 31
An analyst needs to find all events that are creating offenses that are triggered by rules that contain the word suspicious in the rule name.
Which query can the analyst use as a working sample?
- A. SELECT LOGGEDOFFENSE(logsourceid), * from offense_events where RULENAME(creeventlist) ILIKE ,%suspicious%'
- B. SELECT LOGSOURCERULES(logsourceid), " from rule_events where RULENAME(creeventlist) ILIKE '%suspicious%'
- C. SELECT LOGSOURCETYPE(logsourceid), - from log_events where RULENAME(creeventlist) ILIKE '%suspicious%'
- D. SELECT LOGSOURCENAME(logsourceid), * from events where RULENAME(creeventlist) ILIKE
,o/0suspicious%'
Answer: D
NEW QUESTION 32
An analyst wants to analyze the long-term trending of data from a search.
Which chart would be used to display this data on a dashboard?
- A. Scatter Chart
- B. Bar Graph
- C. Time Series chart
- D. Pie Chart
Answer: D
NEW QUESTION 33
An analyst needs to investigate an Offense and navigates to the attached rule(s).
Where in the rule details would the analyst investigate the reason for why the rule was triggered?
- A. Rule responses
- B. Rule actions
- C. List of test conditions
- D. Rules response limiter
Answer: A
NEW QUESTION 34
Which component in QRadar collects and creates flow information?
- A. sflow
- B. Qflow
- C. J-Flow
- D. NetFIow
Answer: B
Explanation:
Explanation
https://www.ibm.com/support/pages/qradar-about-flows-and-difference-between-qflow-collector-and-qradar-eve
NEW QUESTION 35
An analyst is investigating access to sensitive data on a Linux system. Data is accessible from the /secret directory and can be viewed using the 'sudo oaf command. The specific file /secret/file_08-txt was known to be accessed in this way. After searching in the Log Activity Tab, the following results are shown.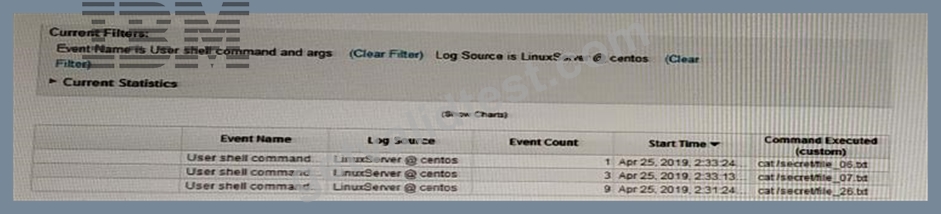
When interpreting this, the analyst is having trouble locating events which show when the file was accessed.
Why could this be?
- A. The 'LinuxServer @ cantos' log source has boon configured as a Faise Positive and the specific event for that file has been dropped.
- B. The 'LinuxServer @ centos' log source has coalescing configured and the specific event for that file can only be accessed by clicking on the 'Event Count' value.
- C. The 'LinuxServer @ centos' log source has not been configured to send the relevant events to QRadar.
- D. The ;LinuxServer @ centos; log source has coalesscing conigured and the specific event for that file has been discardedd.
Answer: B
NEW QUESTION 36
An analyst is working on Offense management and finds that a few of the offenses are not being removed from the Offense tab even after the Offense retention period has elapsed.
What could be the reason that these offenses are not being removed?
- A. Offense is released
- B. Offense is protected
- C. Offense is inactive
- D. Offense has been annotated
Answer: B
Explanation:
Explanation
https://www.ibm.com/docs/en/qsip/7.4?topic=management-offense-retention
NEW QUESTION 37
An analyst needs to create a dashboard item that can be shared with other users. What is the main step in this process?
- A. Create and share the search criteria that the dashboard Item will use.
- B. Have users index the shared search criteria for reuse.
- C. Enable a new custom dashboard and share it with users.
- D. Ask the administrator to modify the shared search criteria and test the dashboard.
Answer: C
NEW QUESTION 38
What does the Assets tab provide?
A unified view of the information that is kwon about:
- A. triggered Offenses.
- B. log sources.
- C. events and flows.
- D. network devices.
Answer: C
Explanation:
Explanation
https://www.ibm.com/docs/en/qradar-on-cloud?topic=administration-asset-management
NEW QUESTION 39
An analyst notices that there are a number of invalid Offenses being created from a network node. This node has been determined to be in Domain 2 and has the following log sources sending it events: (3Com 8800 Series Switch from 172.18.1.1, Cisco ACE Firewall from 172.18.1.2, FireEye from 172.18.1.3, and Palo Alto PA Series from 172.18.1.8).
The analyst should create a False Positive Building Block that has a filter:
- A. "when the remote IP is one of the following 172.18.1.1, 172.18.1.2. 1.3 172. 18.18.1.8
- B. "when the destination IP is in 172.18.0.0/16"
- C. "when the local network is Domain 2 and when the source IP is in 172.18.0.0/16"
- D. "when the local network is Domain 2 and when the source IP is in 172.18.0.0/16"
Answer: D
NEW QUESTION 40
When an Offense is triggered, it only shows the events that triggered the Offense. The analyst wants to investigate further to see more events around the incident, not only those that triggered the Offense. The analyst clicks on the event count and sees the events belonging to the Offense.
How can the analyst processed to see a more detailed picture of what occurred?
- A. Right-click and filter on the Destination IP.
- B. Right-click on the destination IP, and choose More Options, then Raw Events.
- C. Right-click on the source IP, and choose More Options, then Information, and then Search Events
- D. Right-click on the source IP, and choose View in DSM Editor.
Answer: C
NEW QUESTION 41
QRadar collects information from numerous log sources and other agents. Sometimes these agents stop reporting to QRadar for a variety of reasons. There is a default rule in QRadar to help identify these cases called the Device Stopped Sending Events (DSSE) Rule.
What does the DSSE Rule do?
- A. It listens for log sources that send out regular health events and triggers the Rule when encountered
- B. It checks for Rules which have fired due to an absence of Events.
- C. It runs when there is an absence of Events.
- D. It checks for log sources which are reporting that they have not had any communication in a certain amount of time.
Answer: D
NEW QUESTION 42
While creating a new custom property, which is a valid property types selection?
- A. Flow Based
- B. Event Based
- C. AQL Based
- D. Regular Expressions Based
Answer: D
Explanation:
Explanation
https://www.ibm.com/docs/en/qsip/7.4?topic=qradar-custom-property-definitions-in-dsm-editor
NEW QUESTION 43
An analyst needs to review additional information about the Offense top contributors, including notes and annotations that are collected about the Offense.
Where can the analyst review this information?
- A. In the bottom portion of the Offense main view
- B. In the top portion of the Offense Summary window
- C. In the top portion of the Offense main view
- D. In the bottom portion of the Offense Summary window
Answer: A
NEW QUESTION 44
An analyst noticed that from a particular subnet (203.0.113.0/24), all IP addresses are simultaneously trying to reach out to the company's publicly hosted FTP server.
The analyst also noticed that this activity has resulted in a Type B Superflow on the Network Activity tab-Under which category, should the analyst report this issue to the security administrator?
- A. DDoS
- B. Syn Flood
- C. Network Scan
- D. Port Scan
Answer: A
NEW QUESTION 45
How can an analyst verify if any host in the deployment is vulnerable to CVE ID; CVE-2010-000?
- A. Use the asset search feature, select vulnerability external reference from the list of search parameters, select CVE and then type: $2010-000
- B. Use the asset search feature, select vulnerability external reference from the list of search parameters, select CVE and then type: 2010-000
- C. Use the asset search feature, select vulnerability external reference from the list of search parameters, select CVE and then type: $CVE-2010000
- D. Use the asset search feature, select vulnerability external reference from the list of search parameters, select CVE and then type: CVE-2010000
Answer: B
Explanation:
Explanation
You receive a notification that CVE ID: CVE-2010-000 is being actively used in the field. To verify whether any hosts in your deployment are vulnerable to this exploit, you can select Vulnerability External Reference from the list of search parameters, select CVE, and then type the 2010-000 To view a list of all hosts that are vulnerable to that specific CVE ID
https://www.ibm.com/docs/en/SS42VS_7.3.2/com.ibm.qradar.doc/b_qradar_users_guide.pdf
NEW QUESTION 46
An analyst has been assigned a number of Offenses to review and a new event occurs. review and manage.
While reviewing an inactive offense, a new event occurs.
Which statement applies to the Offense?
- A. The event is added in a new Offense that is created.
- B. The event is added to the Offense and the status is changed to Dormant.
- C. The rule that created the Offense is temporarily halted.
- D. The event is added to the Offense and the status is changed to Active.
Answer: B
NEW QUESTION 47
To provide insight into why QRadar considers the event to be threatening, what does QRadar add to the Offense that users cannot edit or delete?
- A. Location
- B. Source IP
- C. Annotations
- D. Attack path
Answer: C
Explanation:
Explanation
https://www.ibm.com/docs/en/qsip/7.4?topic=investigations-investigating-offense-by-using-summary-informatio Annotations provide insight into why QRadar considers the event or observed traffic to be threatening.
QRadar can add annotations when it adds events or flows to an offense. The oldest annotation shows information that QRadar added when the offense was created. Users cannot add, edit, or delete annotations.
NEW QUESTION 48
Which graph types are available for QRadar SIEM reports? (Choose two)
- A. Histogram
- B. Pie
- C. Stacked Bar
- D. Frequency curve
- E. Trivial curve
Answer: B,C
Explanation:
Explanation
https://www.ibm.com/docs/en/qsip/7.4?topic=management-graph-types
NEW QUESTION 49
......
Oct-2021 Latest GetValidTest C1000-018 Exam Dumps with PDF and Exam Engine: https://www.getvalidtest.com/C1000-018-exam.html