


Get Jul-2026 updated Exam FCP_FCT_AD-7.4 Dumps with New Questions
100% Pass Guarantee for FCP_FCT_AD-7.4 Exam Dumps with Actual Exam Questions
NEW QUESTION # 41
An administrator must add an authentication server on FortiClient EMS in a different security zone that cannot allow a direct connection.
Which solution can provide secure access between FortiClient EMS and the Active Directory server?
- A. Configure a slave FortiClient EMS on a virtual machine.
- B. Configure an Active Directory connector between FortiClient EMS and the Active Directory server.
- C. Configure Active Directory and install FortiClient EMS on the same VM.
- D. Configure and deploy a FortiGate device between FortiClient EMS and the Active Directory server.
Answer: D
Explanation:
* Requirement:
* The administrator needs to add an authentication server on FortiClient EMS in a different security zone that cannot allow a direct connection.
* Solution Analysis:
* The goal is to securely connect FortiClient EMS and the Active Directory server despite being in different security zones.
* Evaluating Options:
* Installing FortiClient EMS on the same VM as Active Directory (option B) is not practical due to security zone separation.
* Configuring a slave FortiClient EMS on a virtual machine (option C) does not address the need for secure communication.
* Configuring an Active Directory connector (option D) may not be sufficient without secure routing.
* Conclusion:
* Deploying a FortiGate device between FortiClient EMS and the Active Directory server ensures secure and controlled access between the two zones.
References:
FortiClient EMS and FortiGate configuration and deployment documentation from the study guides.
NEW QUESTION # 42
When multitenancy is enabled on FortiClient EMS, which administrator role can provide access to the global site only? (Choose one answer)
- A. Settings administrator
- B. Standard administrator
- C. Tenant administrator
- D. Global administrator
Answer: A
Explanation:
According to theFortiClient EMS Administration Guide(specifically the sections onMultitenancy), when multitenancy is enabled, the system introduces specific administrator roles to manage the separation between global settings and individual sites.
1. The Settings Administrator Role (Answer B)
* Specific Scope:TheSettings administratoris a specialized role designed to haveaccess to the global site only.
* Permissions:This role can access all configuration options on the global site, with the notable exception ofadministrator configuration(they cannot create or manage other admin accounts).
* Use Case:This is typically used for auditors or system managers who need to oversee global-level configurations without needing access to specific endpoint data within individual sites or the power to modify administrative users.
2. Comparison with Other Multitenancy Roles
* Super administrator:This role hasunlimited accessto the global site andall other siteswithin the EMS instance.
* Site administrator:This role is restricted tospecified sites onlyand hasno access to the global site.
* Standard administrator (Answer C):This is a generic role level within a site or a single-tenant environment but is not the role that defines "global-only" access in a multitenant setup.
* Tenant administrator / Global administrator:While these terms are common in general IT, FortiClient EMS documentation specifically uses the titlesSuper,Settings, andSiteadministrators for multitenancy management.
3. Curriculum References
* FortiClient EMS 7.2/7.4 Study Guide (Multitenancy Chapter):Explicitly lists "Settings administrator" as the role providing access to the global site only.
* Admin Roles Table:The documentation provides a comparison table where the Settings Administrator's scope is strictly defined as "Global site only".
NEW QUESTION # 43
Refer to the exhibit, which shows the endpoint summary information on FortiClient EMS.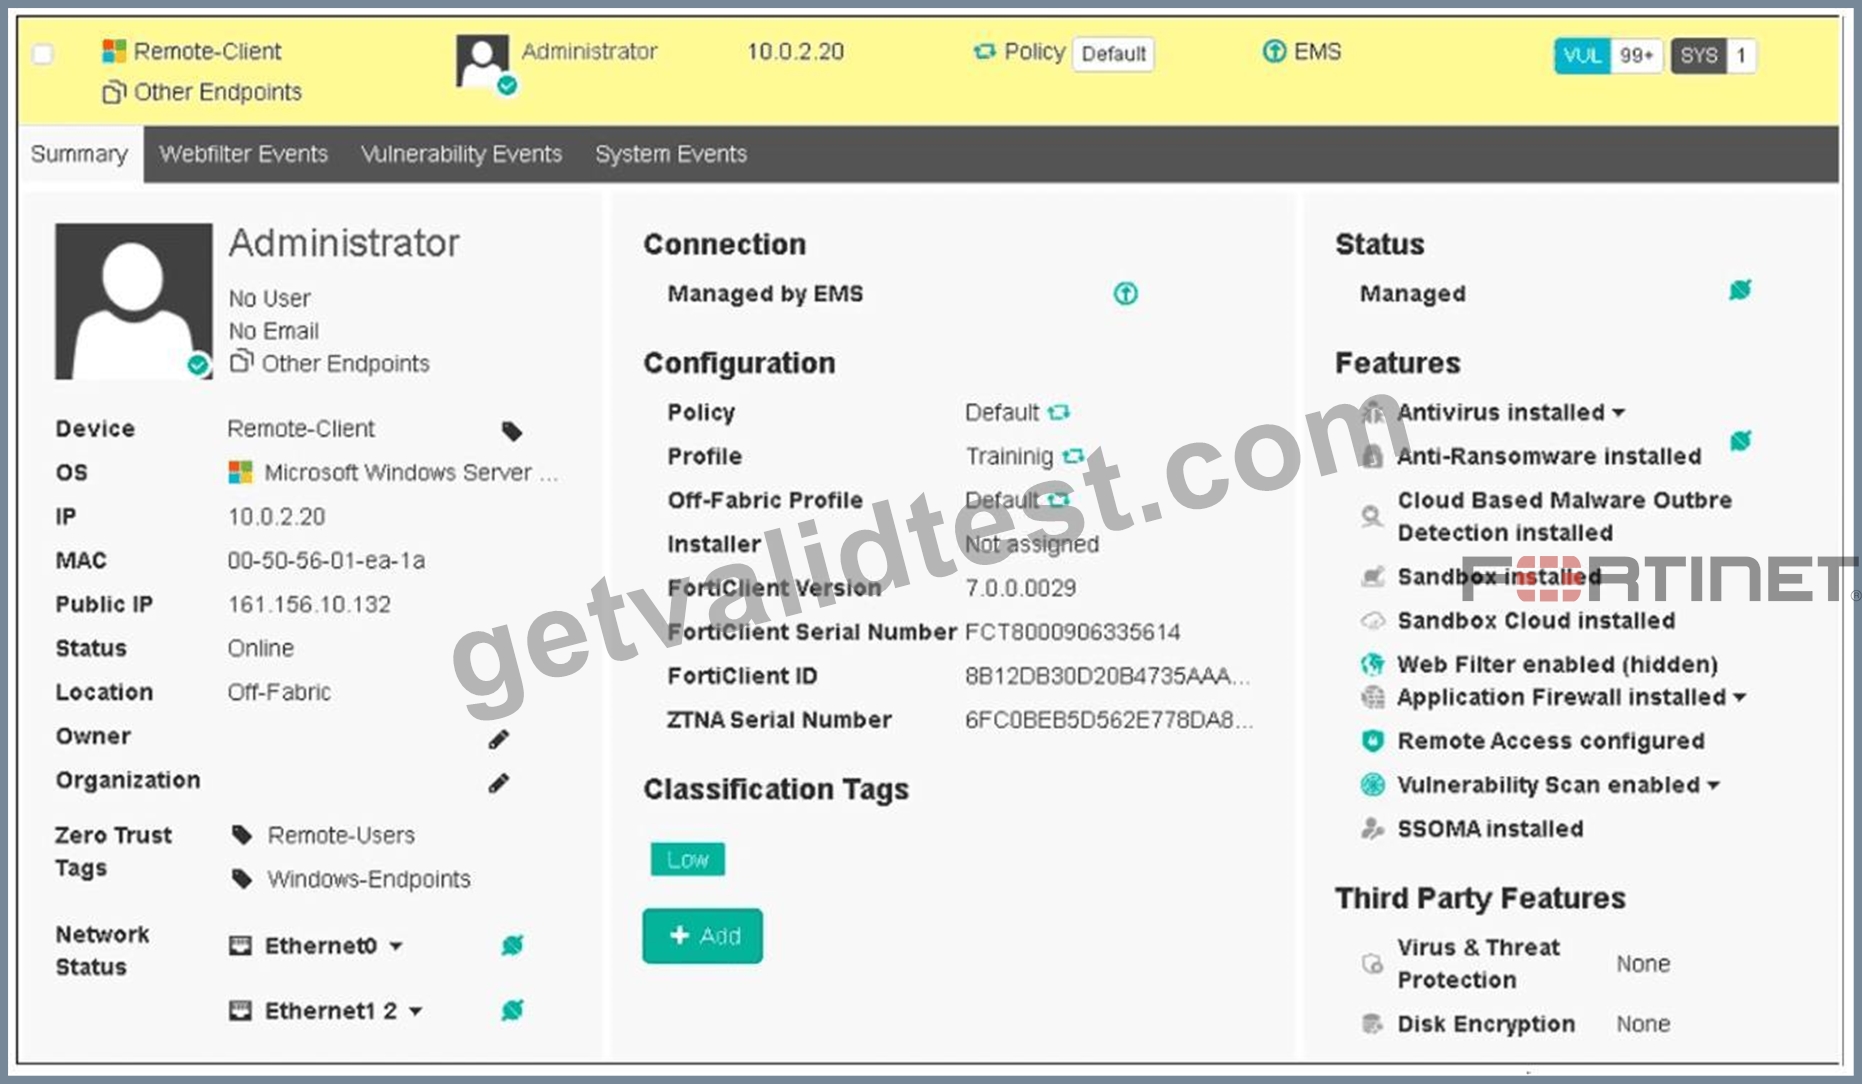
What two conclusions can you make based on the Remote-Client status shown above? (Choose two.)
- A. The endpoint is configured to support FortiSandbox.
- B. The endpoint is currently off-net.
- C. The endpoint has been assigned the Default endpoint policy.
- D. The endpoint is classified as at risk.
Answer: B,C
Explanation:
Based on the Remote-Client status shown in the exhibit:
* Endpoint Policy:The "Policy" field shows "Default," indicating that the endpoint has been assigned the Default endpoint policy.
* Connection Status:The "Location" field shows "Off-Fabric," meaning that the endpoint is currently off the corporate network (off-net).
Therefore, the two conclusions that can be made are:
* The endpoint has been assigned the Default endpoint policy.
* The endpoint is currently off-net.
References
* FortiClient EMS 7.2 Study Guide, Endpoint Summary Information Section
* Fortinet Documentation on Endpoint Policies and Status Indicators
NEW QUESTION # 44
Which security attribute is verified during the SSL connection negotiation between FortiClient and FortiClient EMS to mitigate man-in-the-middle (MITM) attacks? (Choose one answer)
- A. location (L)
- B. organization (O)
- C. serial number (SN)
- D. common name (CN)
Answer: D
Explanation:
According to theFortiClient EMS Administrator Study Guide (7.2/7.4 versions)and theFortinet Document LibraryregardingSSL/TLS Endpoint Communication Security, the primary attribute verified during the SSL connection negotiation to mitigate Man-in-the-Middle (MITM) attacks is theCommon Name (CN).
1. SSL Connection Negotiation & MITM Mitigation
* Verification Process: When FortiClient attempts to establish aTelemetry connectionwith the FortiClient EMS server, an SSL handshake occurs. To ensure it is communicating with the legitimate server and not a malicious interceptor (MITM), FortiClient verifies the server's certificate.
* Role of the Common Name (CN): TheCommon Name(or theSubject Alternative Name - SAN) in the certificate must match theFQDN (Fully Qualified Domain Name)or theIP addressthat the client intended to connect to.
* Security Enforcement: If the CN/SAN does not match the server's expected address, FortiClient will detect a discrepancy. Depending on theInvalid Certificate Actionsetting in the profile (e.g., Warn or Block), it will prevent the establishment of a secure session to stop the MITM attacker from masquerading as the EMS server.
2. Why Other Options are Incorrect/Secondary
* A. Serial Number (SN): While every certificate has a unique Serial Number, it is primarily used by the Certificate Authority (CA) for tracking and revocation purposes. While FortiOS 7.2.4+ can use SN for certain restricted VPN checks, the core SSL negotiation mechanism for identifying a specific host to prevent spoofing relies on theCN/SANfields.
* C. Location (L) and D. Organization (O): These are descriptive fields within the certificate'sSubject that provide geographical and corporate information. They are not functionally used by the SSL/TLS protocol to verify the identity of the host during the connection negotiation or to mitigate MITM attacks.
3. Curriculum References
* EMS Administration Guide (System Settings Profile): Details how the client verifies the EMS server certificate. It specifies that for a connection to be trusted, the server address must align with the certificate's identity fields (CN/SAN).
* FortiGate/FortiOS 7.2.4 New Features: Highlights the specific enhancement where FortiClient EMS connectors now "trust EMS server certificate renewals based on theCN field" to ensure continuous secure communication.
NEW QUESTION # 45
Which component or device shares device status information through ZTNA telemetry?
- A. FortiClient
- B. FortiClient EMS
- C. FortiGate Access Proxy
- D. FortiGate
Answer: A
Explanation:
FortiClient communicates directly with FortiClient EMS to continuously share device status information through ZTNA telemetry.
NEW QUESTION # 46
An administrator must deploy FortiClient for an organization that has BYOD and remote users.
What can the administrator use to deploy FortiClient? (Choose one answer)
- A. FortiClient zero-touch provisioning
- B. Microsoft System Center Configuration Manager (SCCM)
- C. Group Policy Object (GPO)
- D. Microsoft Intune
Answer: D
Explanation:
According to theFortiClient EMS Administrator Study Guideand theFortinet Document Library (7.2/7.4 versions), the most effective method for deploying FortiClient toBYOD (Bring Your Own Device)and remote usersis usingMicrosoft Intune(or other supported Mobile Device Management - MDM solutions).
1. Why Microsoft Intune (Answer C) is the Correct Choice:
* Cloud-Based Accessibility:Unlike GPO or SCCM, which traditionally require a direct connection to the local Active Directory (AD) domain or a VPN to reach the on-premises infrastructure, Microsoft Intune is a cloud-based MDM. This makes it the native choice forremote userswho may not always be on the corporate network.
* BYOD Management:Intune is specifically designed to manage a variety of operating systems (Windows, macOS, iOS, Android) that are common in BYOD environments. It allows administrators to push the FortiClient installation package and enrollment configuration (such as the invitation_code or ems_server details) directly to the user's device via the cloud.
* Integration with EMS:FortiClient EMS 7.2/7.4 provides specific documentation forIntune Integration. Administrators can create a custom MSI or .pkg installer in EMS, upload it to Intune, and use Intune's app configuration policies to automate the Telemetry connection to EMS.
2. Why Other Options are Incorrect for this Scenario:
* A. FortiClient zero-touch provisioning:While FortiClient supports zero-touch provisioning (particularly for mobile or through FortiCloud), in the context of a "deployment tool" for an organization's broad BYOD and remote fleet, it is typically afeatureorprocessfacilitated by an MDM like Intune rather than the standalone deployment mechanism for the initial software package on third- party remote devices.
* B. Microsoft SCCM:SCCM (now part of Microsoft Configuration Manager) is heavily reliant on on- premises infrastructure and is generally used for corporate-owned, domain-joined devices. It is less flexible than Intune for managing "unmanaged" BYOD devices belonging to remote users.
* D. Group Policy Object (GPO):GPO requires the device to be joined to theActive Directory (AD) Domain. BYOD devices are typically not domain-joined, and remote devices cannot receive GPO updates unless they are connected via VPN at the time of the policy refresh, making it unsuitable for this specific use case.
3. Curriculum References:
* EMS Administration Guide (Deployment Section):Specifies that for endpoints not reachable via AD
/Workgroups (which covers remote and BYOD), administrators should use theInstaller Linkmethod or anMDM (like Microsoft Intune).
* Intune Deployment Guide for FortiClient:Detail the specific use ofConfiguration Keys(e.g., cloud_invite_code, ems_server) that are passed from Intune to the FortiClient app to ensure that once the remote user installs the app, it automatically registers to the correct EMS instance.
NEW QUESTION # 47
An administrator needs to connect FortiClient EMS as a fabric connector to FortiGate What is the prerequisite to get FortiClient EMS lo connect to FortiGate successfully?
- A. Import and verify the FortiClient EMS tool CA certificate on FortiGate.
- B. Import and verify the FortiClient client certificate on FortiGate.
- C. Revoke and update the FortiClient EMS root CA.
- D. Revoke and update the FortiClient client certificate on EMS.
Answer: A
Explanation:
* Connecting FortiClient EMS to FortiGate:
* The administrator needs to establish a connection between FortiClient EMS and FortiGate as a fabric connector.
* Prerequisites for Connection:
* A key prerequisite is the import and verification of the FortiClient EMS tool CA certificate on FortiGate to ensure a trusted connection.
* Conclusion:
* The correct prerequisite for a successful connection is to import and verify the FortiClient EMS tool CA certificate on FortiGate.
References:
FortiClient EMS and FortiGate connection and certificate management documentation from the study guides.
NEW QUESTION # 48
Which Fortinet solution can you integrate FortiClient with to use the single sign-on mobility agent (SSOMA) feature? (Choose one answer)
- A. FortiSASE
- B. FortiPAM
- C. FortiAuthenticator
- D. FortiNAC
Answer: C
Explanation:
According to theFortiClient EMS 7.2/7.4 Administration GuideandFortiAuthenticator Study Guides, the Single Sign-On Mobility Agent (SSOMA)is a feature specifically designed to integrate with FortiAuthenticatorto provide transparent, identity-based authentication.
1. Integration with FortiAuthenticator (Answer A)
* The SSOMA Service:The mobility agent service is hosted on theFortiAuthenticatorunit.
Administrators must navigate toFortinet SSO Methods > SSO > Generalon the FortiAuthenticator and toggle onEnable FortiClient SSO Mobility Agent Service.
* Communication Protocol:FortiClient communicates with FortiAuthenticator via a specified TCP listening port (defaulting to8001or8005) and uses apre-shared key(secret key) for authentication.
* Transparent Authentication:Once configured, the SSOMA on the endpoint automatically sends user logon information and IP address changes (such as WiFi roaming) to FortiAuthenticator.
FortiAuthenticator then shares this information with FortiGate units to enforce identity-based security policies without the user needing to re-authenticate manually.
2. Modern Capabilities (Azure AD / Entra ID)
* Cloud Integration:In FortiClient 7.2.1 and later, SSOMA supportsnative Azure AD (Entra ID). In this mode, the agent sends the Azure AD domain and tenant ID directly to FortiAuthenticator, allowing organizations to create identity-based policies for cloud-joined devices.
3. Note on FortiPAM (Option C)
* Recent Updates:While recent FortiClient EMS 7.4 documentation mentions an"Add FortiPAM agent to SSOMA"feature, this is an extension of the existing SSOMA framework. The core product that defines and runs the SSOMA service for general Single Sign-On (SSO) remainsFortiAuthenticator.
4. Why Other Options are Incorrect
* B. FortiSASE:While FortiSASE uses FortiClient for Secure Internet Access (SIA), it uses different mechanisms (like SAML or the SASE cloud portal) for user identity rather than the specific SSOMA agent service.
* D. FortiNAC:FortiNAC uses FortiClient for persistent agent-based posture assessment and scanning, but it does not utilize the SSOMA mobility agent for user-to-IP mapping.
NEW QUESTION # 49
Refer to the exhibit.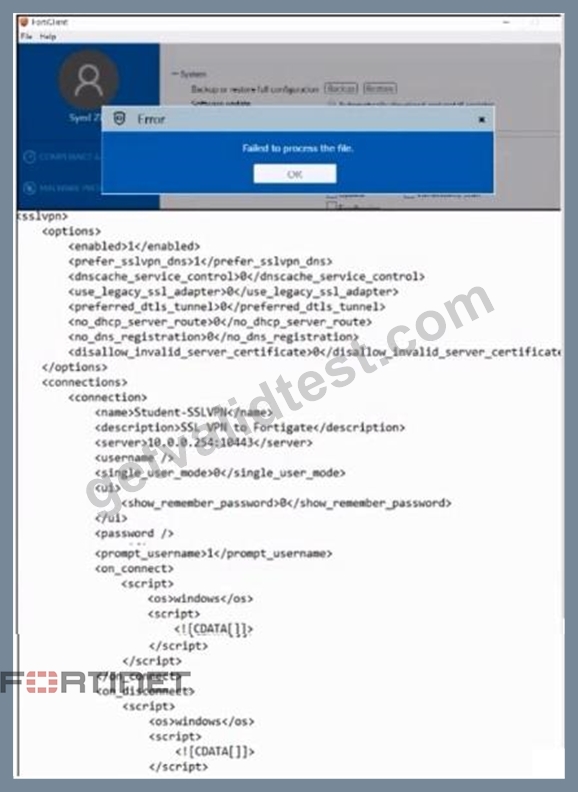
An administrator has restored the modified XML configuration file to FortiClient and sees the error shown in the exhibit.
Based on the XML settings shown in the exhibit, what must the administrator do to resolve the issue with the XML configuration file?
- A. The administrator must resolve the XML syntax error.
- B. The administrator must save the file as FortiClient-config conf.
- C. The administrator must change the file size
- D. The administrator must use a password to decrypt the file
Answer: A
Explanation:
Based on the error message and the XML configuration file shown in the exhibit:
* The error "Failed to process the file" typically indicates an issue with the XML syntax.
* Upon reviewing the XML content, it is crucial to ensure that all tags are correctly formatted, properly opened and closed, and that there are no syntax errors.
* Resolving any XML syntax errors will allow FortiClient to successfully process and restore the configuration file.
Therefore, the administrator must resolve the XML syntax error to fix the issue.
References
* FortiClient EMS 7.2 Study Guide, Configuration File Management Section
* General XML Syntax Guidelines and Best Practices
NEW QUESTION # 50
Refer to the exhibit.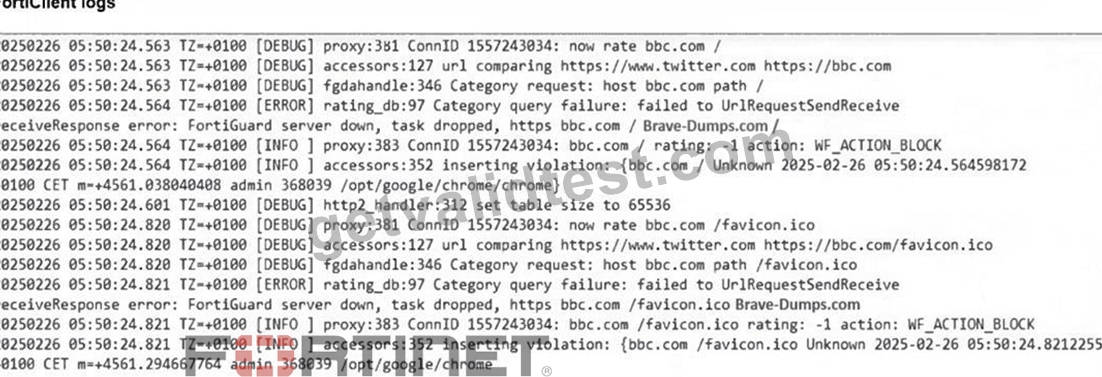
Why is the user not able to access bbc.com? (Choose one answer)
- A. The endpoint cannot resolve the URL FQDN.
- B. The URL is blocked by the web filter endpoint profile.
- C. The application firewall is blocking Google Chrome.
- D. FortiGuard servers are not reachable from the endpoint.
Answer: D
Explanation:
Based on theFortiClient EMS Administrator Study GuideregardingWeb Filtertroubleshooting and the specific log entries provided in the exhibit, the reason the user cannot access the website is due to connectivity issues with FortiGuard.
1. Analysis of the FortiClient Logs:
* The Error Message:The logs show multiple [ERROR] entries stating: rating_db:97 Category query failure: failed to UrlRequestSendReceive.
* Root Cause Identity:The log explicitly describes the failure: receiveResponse error: FortiGuard server down, task dropped, https bbc.com.
* Resulting Action:Because the endpoint could not receive a rating from the FortiGuard servers, the Web Filter module recorded rating: -1 and applied the action WF_ACTION_BLOCK.
2. Why Option C is Correct:
* FortiGuard Dependency:FortiClient's Web Filter module relies on real-time queries to FortiGuard distribution servers to categorize URLs. If the endpoint is behind a firewall blocking FortiGuard ports (typically UDP 53 or 8888, or HTTPS 443) or has no internet path to these servers, it cannot categorize the site.
* Fail-Safe Behavior:In many FortiClient configurations, if a rating cannot be obtained (Category query failure), the default security posture is to block the request to ensure no potentially malicious or unrated
"Unknown" sites are accessed. The logs confirm this by showing the "FortiGuard server down" message immediately followed by the block action.
3. Why Other Options are Incorrect:
* A. The URL is blocked by the web filter endpoint profile:If it were a standard profile block, the log would show a specificCategory ID(e.g., Category 52 for News and Media) being blocked by policy.
Instead, it shows arating failure (-1).
* B. The endpoint cannot resolve the URL FQDN:The logs show the process correctly identifies host bbc.com. If DNS had failed, the proxy wouldn't even reach the stage of attempting a FortiGuard category query for that specific URL.
* D. The application firewall is blocking Google Chrome:While the log mentions /opt/google/chrome
/chrome, the error is generated by the rating_db and proxy components of the Web Filter, not the Application Firewall module.
NEW QUESTION # 51
An administrator configures ZTNA configuration on the FortiGate. Which statement is true about the firewall policy?
- A. It redirects the client request to the access proxy.
- B. It defines ZTNA server.
- C. It only uses ZTNA tags to control access for endpoints.
- D. It uses the access proxy.
Answer: A
Explanation:
"The firewall policy matches and redirects client requests to the access proxy VIP"https://docs.fortinet.com
/document/fortigate/7.0.0/new-features/194961/basic-ztna-configuration
NEW QUESTION # 52
An administrator deploys a FortiClient installation through the Microsoft AD group policy After installation is complete all the custom configuration is missing.
What could have caused this problem?
- A. FortiClient does not have permission to access the distribution package.
- B. The FortiClient package is not assigned to the group
- C. The FortiClient MST file is missing from the distribution package
- D. The FortiClient exe file is included in the distribution package
Answer: B
Explanation:
When deploying FortiClient via Microsoft AD Group Policy, it is essential to ensure that the deployment package is correctly assigned to the target group. The absence of custom configuration after installation can be due to several reasons, but the most likely cause is:
* Deployment Package Assignment:The FortiClient package must be assigned to the appropriate group in Group Policy Management. If this step is missed, the installation may proceed, but the custom configurations will not be applied.
Thus, the administrator must ensure that the FortiClient package is correctly assigned to the group to include all custom configurations.
References
* FortiClient EMS 7.2 Study Guide, Deployment and Installation Section
* Fortinet Documentation on FortiClient Deployment using Microsoft AD Group Policy
NEW QUESTION # 53
What action does FortiClient anti-exploit detection take when it detects exploits?
- A. Patches the compromised application process
- B. Blocks memory allocation to the compromised application process
- C. Terminates the compromised application process
- D. Deletes the compromised application process
Answer: A
Explanation:
The anti-exploit detection protects vulnerable endpoints from unknown exploit attacks. FortiClient monitors the behavior of popular applications, such as web browsers (Internet Explorer, Chrome, Firefox, Opera), Java
/Flash plug-ins, Microsoft Office applications, and PDF readers, to detect exploits that use zero-day or unpatched vulnerabilities to infect the endpoint. Once detected, FortiClient terminates the compromised application process.
NEW QUESTION # 54
Refer to the exhibits.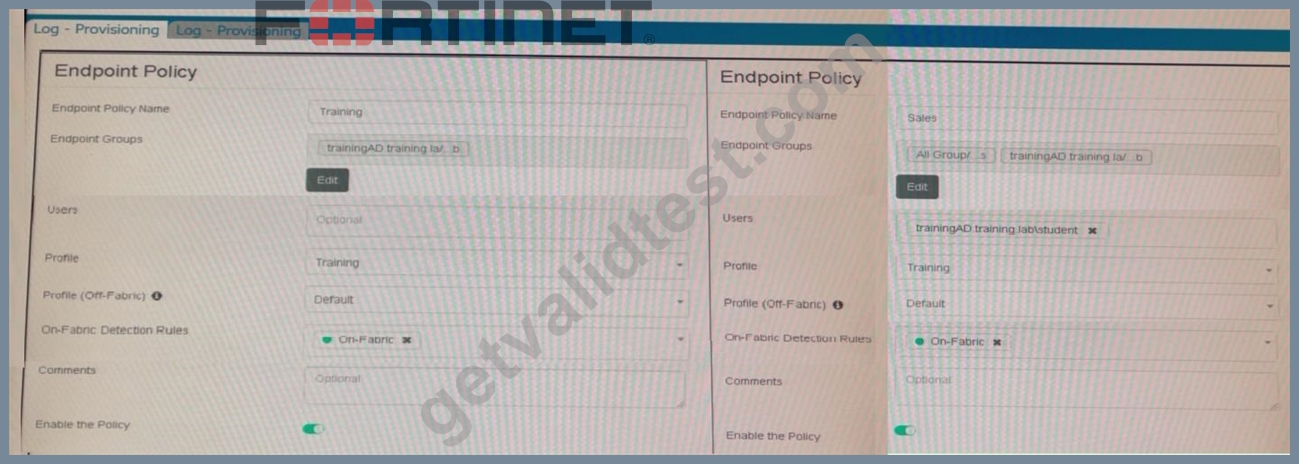

Which shows the configuration of endpoint policies.
Based on the configuration, what will happen when someone logs in with the user account student on an endpoint in the trainingAD domain?
- A. FortiClient EMS will assign the Training policy for on-fabric endpoints and the Sales policy for the off- fabric endpoint
- B. FortiClient EMS will assign the Default policy
- C. B. FortiClient EMS will assign the Training policy
- D. FortiClient EMS will assign the Sales policy
Answer: C
Explanation:
Based on the configuration shown in the exhibits:
* There are three endpoint policies configured: Training, Sales, and Default.
* The "Training" policy is assigned to the "trainingAD.training.lab" group.
* The "Sales" policy is assigned to "All Groups" and "trainingAD.training.lab/student."
* The "Default" policy has no specific groups assigned.
When someone logs in with the user account "student" on an endpoint in the "trainingAD" domain:
* The "Training" policy is specifically assigned to the "trainingAD.training.lab" group.
* The "Sales" policy includes "trainingAD.training.lab/student" but not the general "trainingAD.training.
lab" group.
* The system will prioritize the most specific match for the group.
Therefore, FortiClient EMS will assign the "Training" policy to the "student" account logging into the
"trainingAD" domain as it matches the group "trainingAD.training.lab" directly.
References
* FortiClient EMS 7.2 Study Guide, Endpoint Policy Configuration Section
* FortiClient EMS Documentation on Group Policy Assignment and Matching
NEW QUESTION # 55
Which statement about FortiClient comprehensive endpoint protection is true?
- A. It helps to safeguard systems from email spam
- B. lt helps to safeguard systems from advanced security threats, such as malware.
- C. It helps to safeguard systems from data loss.
- D. It helps to safeguard systems from DDoS.
Answer: B
Explanation:
FortiClient provides comprehensive endpoint protection for your Windows-based, Mac-based, and Linuxbased desktops, laptops, file servers, and mobile devices such as iOS and Android. It helps you to safeguard your systems with advanced security technologies, all of which you can manage from a single management console.
NEW QUESTION # 56
Which component or device shares ZTNA tag information through Security Fabric integration?
- A. FortiGate Access Proxy
- B. FortiGate
- C. FortiClient
Answer: B
Explanation:
FortiClient EMS is the component that shares ZTNA tag information through Security Fabric integration.
ZTNA tags are synchronized from FortiClient EMS as inputs for the FortiGate application gateway. They can be used in ZTNA policies as security posture checks to ensure certain security criteria are met. FortiClient EMS can share ZTNA tags across multiple devices in the Fabric, such as FortiGate, FortiManager, and FortiAnalyzer. FortiClient EMS can also share ZTNA tags across multiple VDOMs on the same FortiGate device. FortiClient EMS can be configured to control the ZTNA tag sharing behavior in the Fabric Devices settings1.
FortiGate is the device that enforces ZTNA policies using ZTNA tags. FortiGate can receive ZTNA tags from FortiClient EMS via Fabric Connector. FortiGate can also publish ZTNA services through the ZTNA portal, which allows users to access applications without installing FortiClient. FortiGate can also provide ZTNA inline CASB for SaaS application access control2.
FortiGate Access Proxy is a feature that enables FortiGate to act as a proxy for ZTNA traffic. FortiGate Access Proxy can be deployed in front of the application servers to provide ZTNA protection. FortiGate Access Proxy can also be deployed behind the application servers to provide ZTNA visibility. FortiGate Access Proxy can use ZTNA tags to identify and authenticate users and devices2.
FortiClient is the endpoint software that connects to ZTNA services. FortiClient can register ZTNA tags with FortiClient EMS based on the endpoint security posture. FortiClient can also use ZTNA tags to access ZTNA services published by FortiGate. FortiClient can also use ZTNA tags to access SaaS applications with ZTNA inline CASB2.
References :=
* Technical Tip: Behavior of ZTNA Tags shared across multiple vdoms or multiple FortiGate firewalls in the Security Fabric connected to the same FortiClient EMS Server
* Synchronizing FortiClient ZTNA tags
* Zero Trust Network Access (ZTNA) to Control Application Access
NEW QUESTION # 57
What is the function of the quick scan option on FortiClient?
- A. It allows users to select a specific file folder on their local hard disk drive (HDD), to scan for threats.
- B. It scans programs and drivers that are currently running, for threats
- C. It scans executable files. DLLs, and drivers that are currently running, for threats.
- D. It performs a full system scan including all files, executable files. DLLs, and drivers for throats.
Answer: D
Explanation:
* Understanding Quick Scan Function:
* The quick scan option on FortiClient is designed to scan certain elements of the system quickly for threats.
* Evaluating Scan Scope:
* The quick scan specifically targets executable files, DLLs, and drivers that are currently running, providing a rapid assessment of the active components of the system.
* Conclusion:
* The correct answer is D, as it accurately describes the function of the quick scan option on FortiClient.
References:
FortiClient scanning options documentation from the study guides.
NEW QUESTION # 58
A company must integrate the FortiClient EMS with their existing identity management infrastructure for user authentication, and implement and enforce administrative access with multi-factor authentication (MFA).
Which two authentication methods can they use in this scenario? (Choose two answers)
- A. SAML
- B. TACACS
- C. RADIUS
- D. LDAPS
Answer: A,C
Explanation:
According to theFortiClient EMS 7.4 Administration Guide, for an organization to integrate with an identity management infrastructure while enforcing administrative access with Multi-Factor Authentication (MFA), the primary supported methods for remote administrator authentication areRADIUSandSAML.
1. RADIUS (Answer B)
* Identity Integration:FortiClient EMS allows administrators to addRADIUS serversas an authentication source under theAdministration > Authentication Serverssection.
* MFA Support:RADIUS is a standard protocol for enforcing MFA. In this scenario, FortiClient EMS acts as a RADIUS client to an external MFA provider (such as FortiAuthenticator, RSA Authentication Manager, or Duo).
* Workflow:When an administrator attempts to log in to the EMS console, EMS sends an Access- Request to the RADIUS server. If the provider requires MFA, it can challenge the user (via push notification or token code) before sending an Access-Accept back to EMS.
2. SAML (Answer D)
* Modern Identity Management:SAML (Security Assertion Markup Language) is the preferred method for integrating with modern cloud and on-premises Identity Providers (IdPs) likeMicrosoft Entra ID (formerly Azure AD),Okta,AD FS, orFortiAuthenticator.
* Native MFA Enforcement:By using SAML SSO, the authentication and MFA process are handled entirely by the IdP. The EMS server acts as the Service Provider (SP). When an admin logs in, they are redirected to the IdP, where the company's existing MFA policies (Conditional Access, etc.) are enforced before the user is granted access back to the EMS console.
* EMS Configuration:The curriculum details specific SAML SSO configurations for various IdPs under theSAML SSOsection of the Administration Guide.
3. Why Other Options are Incorrect/Insufficient
* A. LDAPS:While FortiClient EMS supports importing users fromActive Directory (ADDS)via LDAP
/LDAPS for endpoint management and basic admin login, standard LDAPS does not natively support or enforce an MFA challenge-response workflow in the same integrated way that RADIUS or SAML does for administrative console access.
* C. TACACS:TACACS+ is primarily used for device administration on networking equipment (like FortiGate) and is not a listed or standard method for administrative authentication within the FortiClient EMS software documentation.
NEW QUESTION # 59
Refer to the exhibit.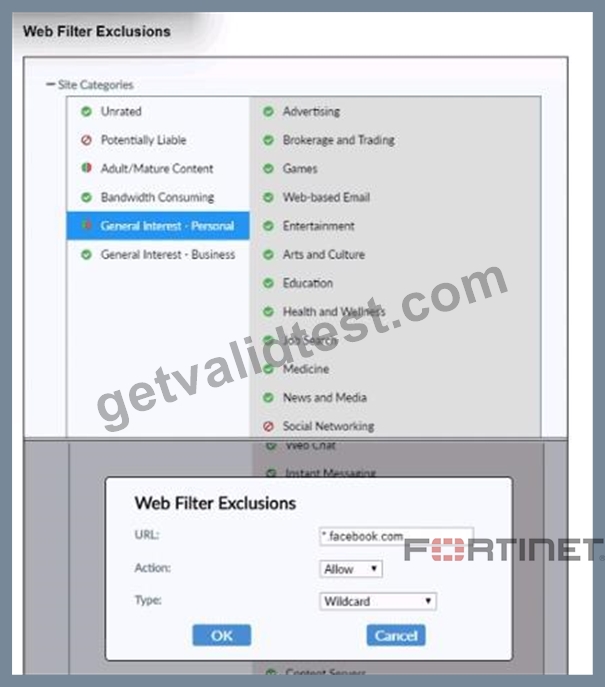
Based on the settings shown in the exhibit, which action will FortiClient take when users try to access www facebook com?
- A. FortiClient will allow access to Facebook.
- B. FortiClient will block access to Facebook and its subdomains.
- C. FortiClient will monitor only the user's web access to the Facebook website
- D. FortiClient will prompt a warning message to want the user before they can access the Facebook website
Answer: B
Explanation:
* Observation of Web Filter Exclusions:
* The exhibit shows a web filter exclusion for "*.facebook.com" with the action set to "Allow."
* Evaluating Actions:
* This configuration means that FortiClient will allow access to Facebook and its subdomains.
* Conclusion:
* When users try to access "www.facebook.com," FortiClient will allow the access based on the web filter exclusion settings.
References:
FortiClient web filter configuration and exclusion documentation from the study guides.
NEW QUESTION # 60
Refer to the exhibit, which shows the Zero Trust Tagging Rule Set configuration.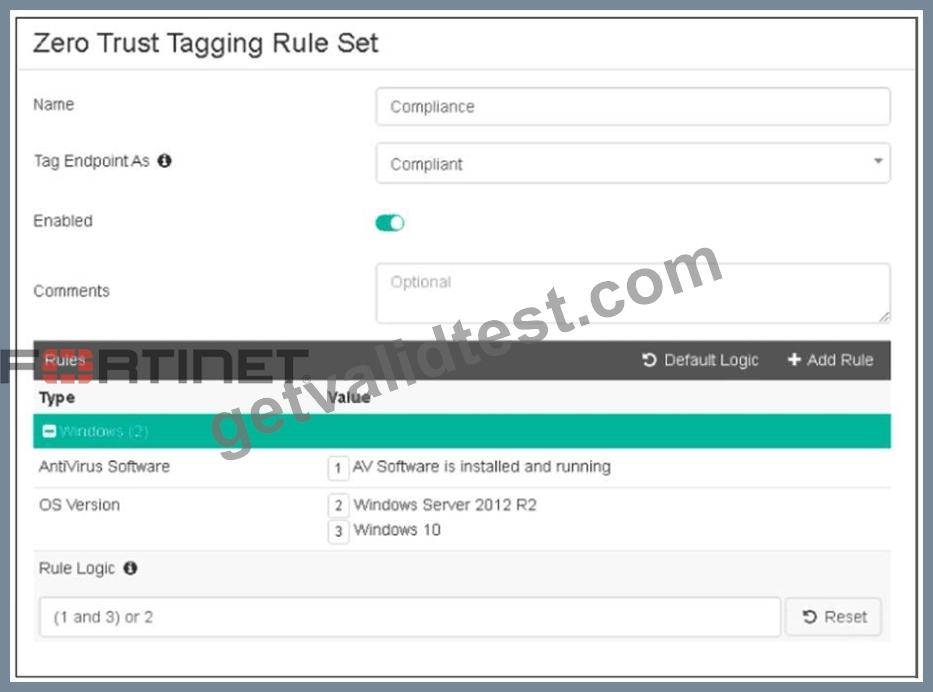
Which two statements about the rule set are true? (Choose two.)
- A. The endpoint must satisfy that only Windows Server 2012 R2 is running.
- B. The endpoint must satisfy that only AV software is installed and running.
- C. The endpoint must satisfy that only Windows 10 is running.
- D. The endpoint must satisfy that antivirus is installed and running and Windows 10 is running.
Answer: A,D
Explanation:
Based on the Zero Trust Tagging Rule Set configuration shown in the exhibit:
* The rule set includes two conditions:
* AV Software is installed and running
* OS Version is Windows Server 2012 R2 or Windows 10
* The Rule Logic is specified as "(1 and 3) or 2," meaning:
* The endpoint must have antivirus software installed and running and must be running Windows
10.
* Alternatively, the endpoint must be running Windows Server 2012 R2.
Therefore, the endpoint must satisfy either:
* Antivirus is installed and running and Windows 10 is running.
* Windows Server 2012 R2 is running.
References
* FortiClient EMS 7.2 Study Guide, Zero Trust Tagging Rule Set Configuration Section
* Fortinet Documentation on Configuring Zero Trust Tagging Rules and Logic
NEW QUESTION # 61
Exhibit.
Based on the FortiClient logs shown in the exhibit, which endpoint profile policy is currently applied lo the ForliClient endpoint from the EMS server?
- A. Default
- B. Fortinet-Training
- C. Default configuration policy c
- D. Compliance rules default
Answer: B
Explanation:
* Observation of Logs:
* The logs show a policy named "Fortinet-Training" being applied to the endpoint.
* Evaluating Policies:
* The log entries indicate that the "Fortinet-Training" policy was received and applied.
* Conclusion:
* Based on the logs, the currently applied policy on the FortiClient endpoint is "Fortinet-Training".
References:
FortiClient EMS policy configuration and log analysis documentation from the study guides.
NEW QUESTION # 62
Refer to the exhibit.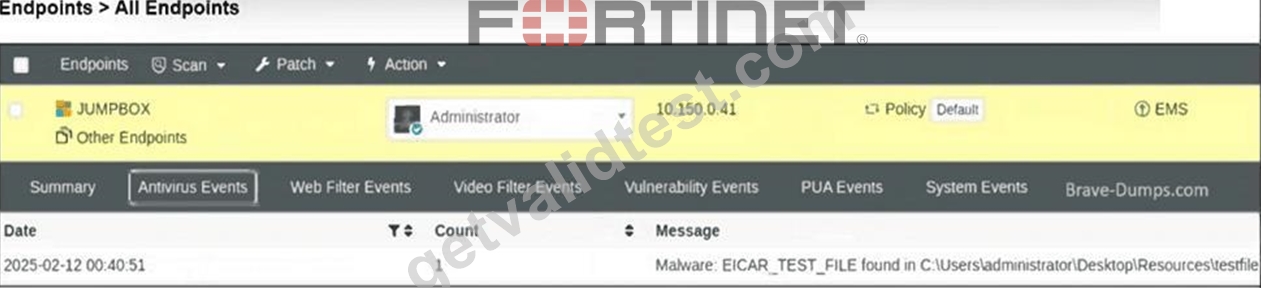
You provide a webserver hosting service. An endpoint downloads a test file, testfile.txt, that gets blocked by FortiClient.
Which configuration can you use to make the file accessible on the endpoint? (Choose one answer)
- A. Add the file to the allowlist in quarantine management on FortiClient EMS.
- B. Exclude testfile.txt from the malware protection profile.
- C. Restore access to file directly using FortiClient.
- D. Allow the webserver URL in the exclusion list in the web filter profile.
Answer: A
Explanation:
According to theFortiClient EMS 7.2/7.4 Administration Guide(specifically theQuarantine Management andMalware Protectionsections), the correct administrative workflow to restore a blocked file and ensure it is no longer flagged as malicious is to use theQuarantine Managementfeature on the EMS server.
1. Analysis of the Exhibit
* Event Type:The exhibit shows anAntivirus Eventwhere a file named testfile.txt was flagged as Malware: EICAR_TEST_FILE.
* Location:The file was found in a local user directory (C:
\Users\administrator\Desktop\Resources\testfile.txt).
* System State:The endpoint is managed by EMS (indicated by thePolicy: DefaultandEMSstatus icons).
2. Why Option D is the Correct Choice:
* Centralized Control:In a managed environment, the administrator uses the EMS console to oversee security incidents. To restore a file that has been quarantined, the administrator must navigate to Quarantine Management > Files.
* Allowlist & Restore Action:By selecting the specific blocked file (testfile.txt) and clickingAllowlist & Restore, two things happen simultaneously:
* Restoration:EMS sends a command to the FortiClient endpoint to release the file from the local quarantine folder and return it to its original path.
* Allowlisting:The file's hash is added to theAllowlist(managed underQuarantine Management > Allowlist), which prevents FortiClient from re-quarantining the file during future real-time or on- demand scans.
* Accessibility:This is the documented method to make a file "accessible on the endpoint" while ensuring it is not immediately re-blocked by the security engine.
3. Why Other Options are Incorrect:
* A. Restore access directly using FortiClient:While FortiClient has a local quarantine tab, the
"Release" button is typicallygreyed outor restricted when the client is managed by EMS to ensure centralized security policy enforcement.
* B. Allow the webserver URL in the exclusion list:The exhibit shows anAntivirus/Malwareevent, not aWeb Filterevent. The file has already been downloaded to the local disk and is being blocked by the Real-Time Protectionengine, so a Web Filter URL exclusion would have no effect on the local file block.
* C. Exclude testfile.txt from the malware protection profile:While adding a path exclusion to the Malware Protection profile is a valid way to prevent future scans of a directory, it doesnot automatically restorea file that hasalreadybeen moved to quarantine. The proper workflow for an existing block is to use the Quarantine Management tool first.
NEW QUESTION # 63
......
FCP_FCT_AD-7.4 exam dumps with real Fortinet questions and answers: https://www.getvalidtest.com/FCP_FCT_AD-7.4-exam.html
Today Updated FCP_FCT_AD-7.4 Exam Dumps Actual Questions: https://drive.google.com/open?id=1k1w8lVt_n9UqGPXVU3TCsB3fCOPSeWFv