


Get Latest Apr-2024 Real MS-102 Exam Questions and Answers FREE
Truly Beneficial For Your Microsoft Exam (Updated 410 Questions)
Microsoft MS-102 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
| Topic 7 |
|
| Topic 8 |
|
| Topic 9 |
|
| Topic 10 |
|
NEW QUESTION # 168
Which role should you assign to User1?
Available Choices (select all choices that are correct)
- A. Records Management
- B. Security Administrator
- C. Security Reader
- D. Hygiene Management
Answer: C
Explanation:
Explanation
A user named User1 must be able to view all DLP reports from the Microsoft 365 admin center.
Users with the Security Reader role have global read-only access on security-related features, including all information in Microsoft 365 security center, Azure Active Directory, Identity Protection, Privileged Identity Management, as well as the ability to read Azure Active Directory sign-in reports and audit logs, and in Office
365 Security & Compliance Center.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/users-groups-roles/directory-assign-admin-roles
NEW QUESTION # 169
Your company has a hybrid deployment of Microsoft 365.
An on-premises user named User1 is synced to Azure AD.
Azure AD Connect is configured as shown in the following exhibit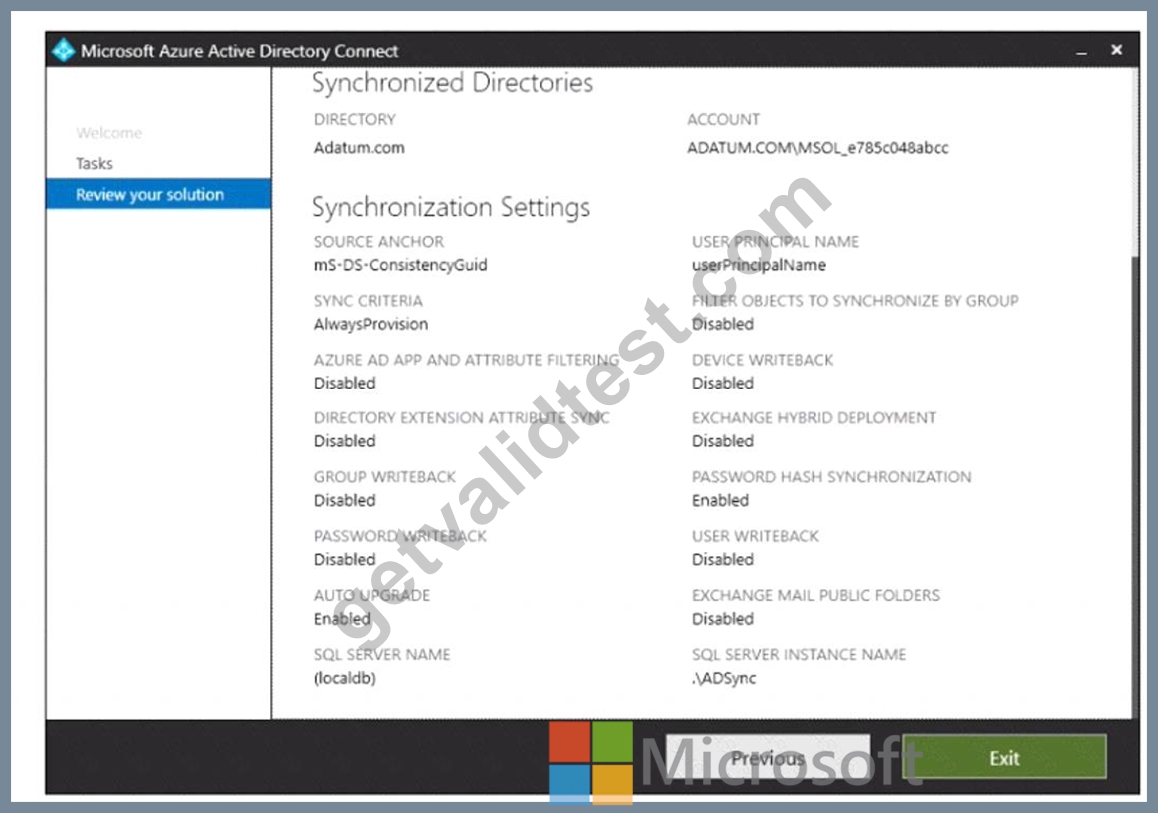
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: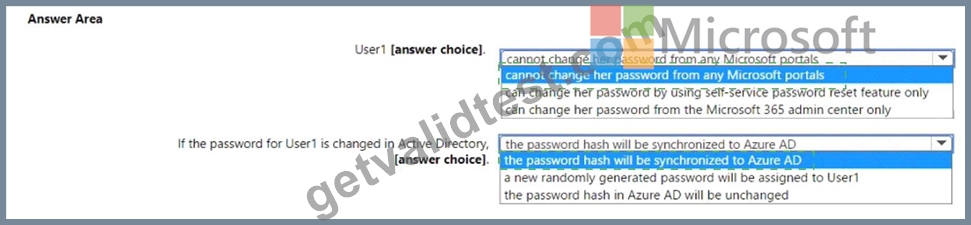
Explanation
NEW QUESTION # 170
You have a Microsoft 365 E5 subscription that uses Microsoft Defender for Cloud Apps.
You need to create a policy that will generate an email alert when a banned app is detected requesting permission to access user information or data in the subscription.
What should you configure? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.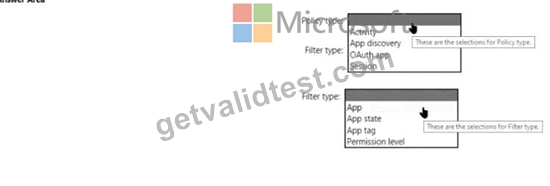
Answer:
Explanation: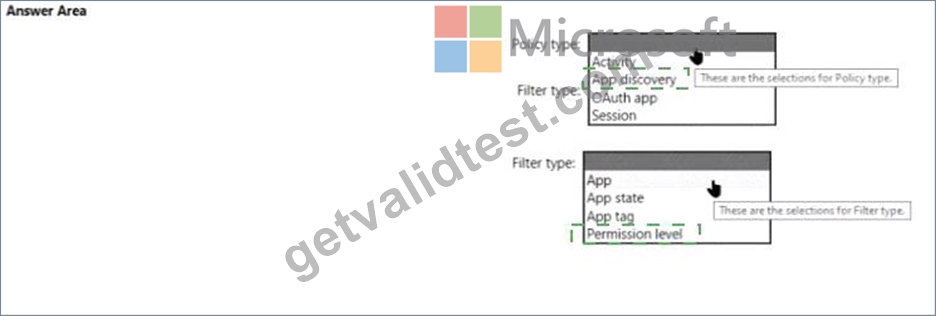
Explanation
NEW QUESTION # 171
You have an Azure AD tenant and a Microsoft 365 E5 subscription. The tenant contains the users shown in the following table.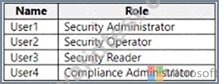
You plan to implement Microsoft Defender for Endpoint.
You verify that role-based access control (RBAC) is turned on in Microsoft Defender for Endpoint.
You need to identify which user can view security incidents from the Microsoft 365 Defender portal.
Which user should you identify?
- A. User2
- B. User4
- C. User3
- D. User1
Answer: D
NEW QUESTION # 172
You need to meet the requirement for the legal department.
Which three actions should you perform in sequence from the Security & Compliance admin center? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.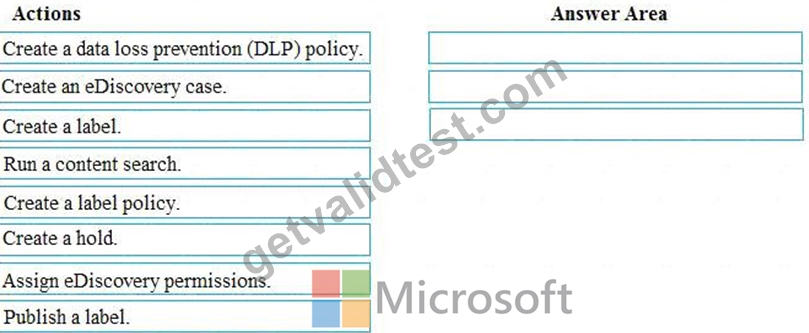
Answer:
Explanation: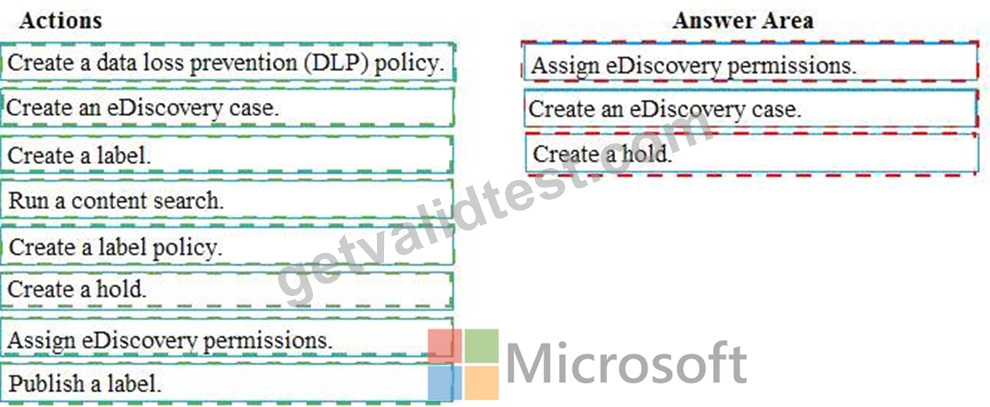
Explanation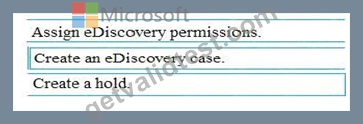
References:
https://www.sherweb.com/blog/ediscovery-office-365/
NEW QUESTION # 173
You have a Microsoft 365 E5 subscription that contains the devices shown in the following table.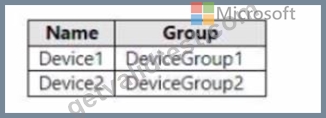
At 08:00. you create an incident notification rule that has the following configurations:
* Name: Notification!
* Notification settings
o Notify on alert seventy: Low
o Device group scope: All (3)
o Details: First notification per incident
* Recipients: [email protected], [email protected]
At 08:02. you create an incident notification rule that has the following configurations:
* Name: Notification
* Notification settings
o Notify on alert severity: Low. Medium
o Device group scope: DevtceGroup1, DeviceGroup2
* Recipients: [email protected]
in Microsoft 365 Defender, alerts are logged as shown in the following table.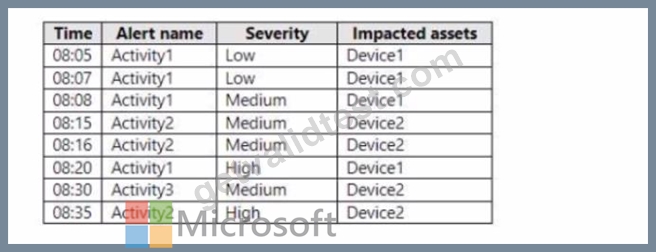
For each of the following statements, select Yes if the statement is true. Otherwise, select No1.
NOTE: Each correct selection is worth one point.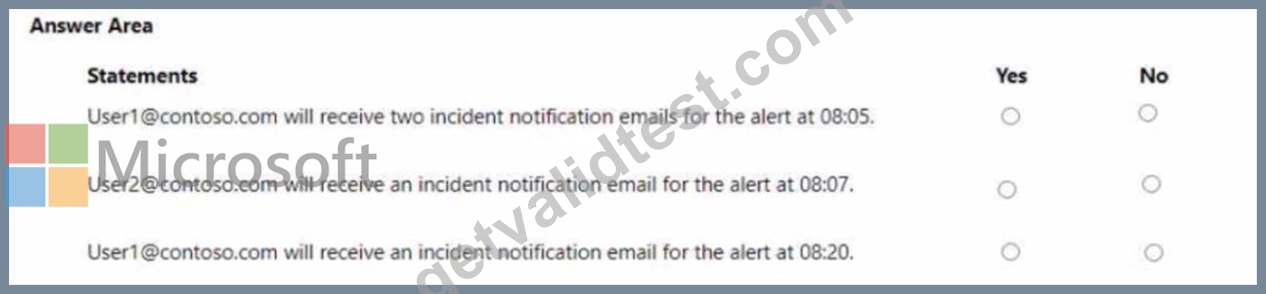
Answer:
Explanation:
NEW QUESTION # 174
You have a Microsoft 365 E5 subscription that uses Microsoft Intune and contains the devices shown in the following table.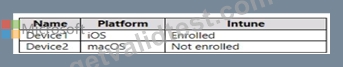
You need to onboard Device1 and Device2 to Microsoft Defender for Endpoint.
What should you use to onboard each device? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: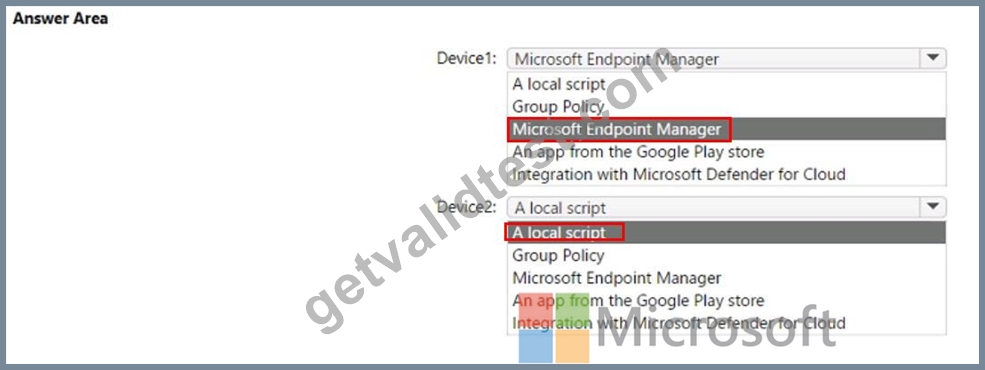
NEW QUESTION # 175
You need to ensure that User2 can review the audit logs. The solutions must meet the technical requirements.
To which role group should you add User2, and what should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.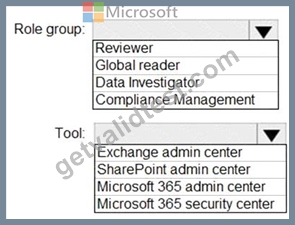
Answer:
Explanation: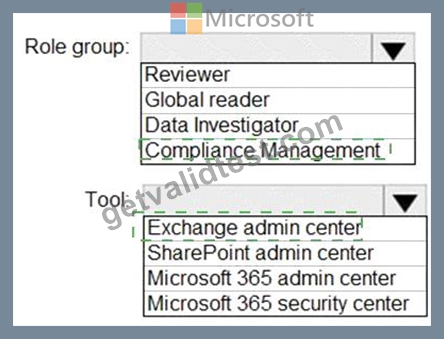
Explanation
Graphical user interface, text Description automatically generated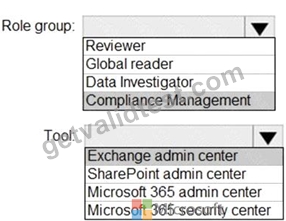
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/search-the-audit-log-in-security-and-compliance?vie
NEW QUESTION # 176
Your company has a Azure AD tenant named comoso.onmicrosoft.com that contains the users shown in the following table.
You need to identify which users can perform the following administrative tasks:
* Reset the password of User4.
* Modify the value for the manager attribute of User4.
Which users should you identify for each task? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.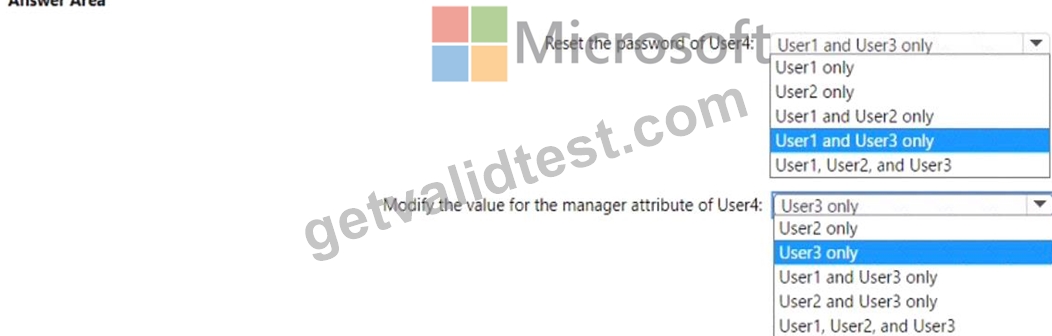
Answer:
Explanation: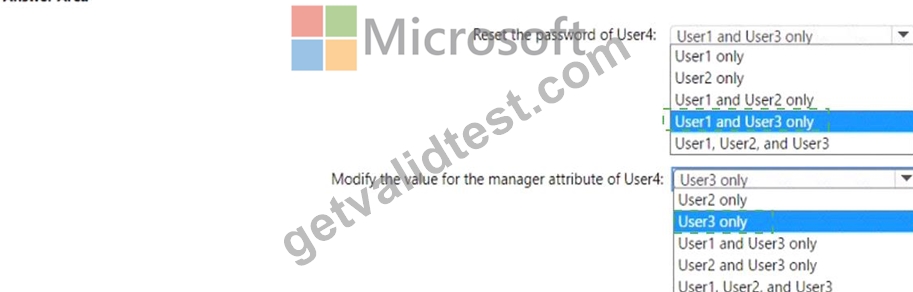
Explanation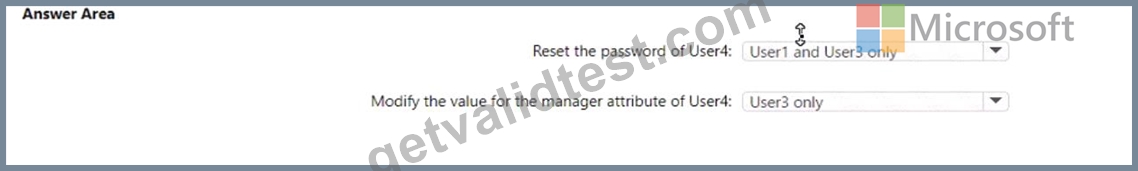
NEW QUESTION # 177
You need to configure Office on the web to meet the technical requirements.
What should you do?
- A. Enable sensitivity labels for Office files in SharePoint Online and OneDrive.
- B. Configure an auto-labeling policy to apply the sensitivity labels.
- C. Assign the Office apps admin role to User1.
- D. Assign the Global reader role to User1.
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels-sharepoint-onedrive-files?view=o3
NEW QUESTION # 178
You have a Microsoft Azure Active Directory (Azure AD) tenant named Contoso.com.
You create a Microsoft Defender for identity instance Contoso.
The tenant contains the users shown in the following table.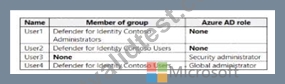
You need to modify the configuration of the Defender for identify sensors.
Solutions: You instruct User3 to modify the Defender for identity sensor configuration.
Does this meet the goal?
- A. Yes
- B. No
Answer: A
NEW QUESTION # 179
You have a Microsoft 365 E5 subscription that contains a Microsoft SharePoint site named Sitel. You need to perform the following tasks:
* Create a sensitive info type named SIT1 based on a regular expression.
* Add a watermark to all new documents that are matched by SIT1.
Which two settings should you use in the Microsoft Purview compliance portal? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: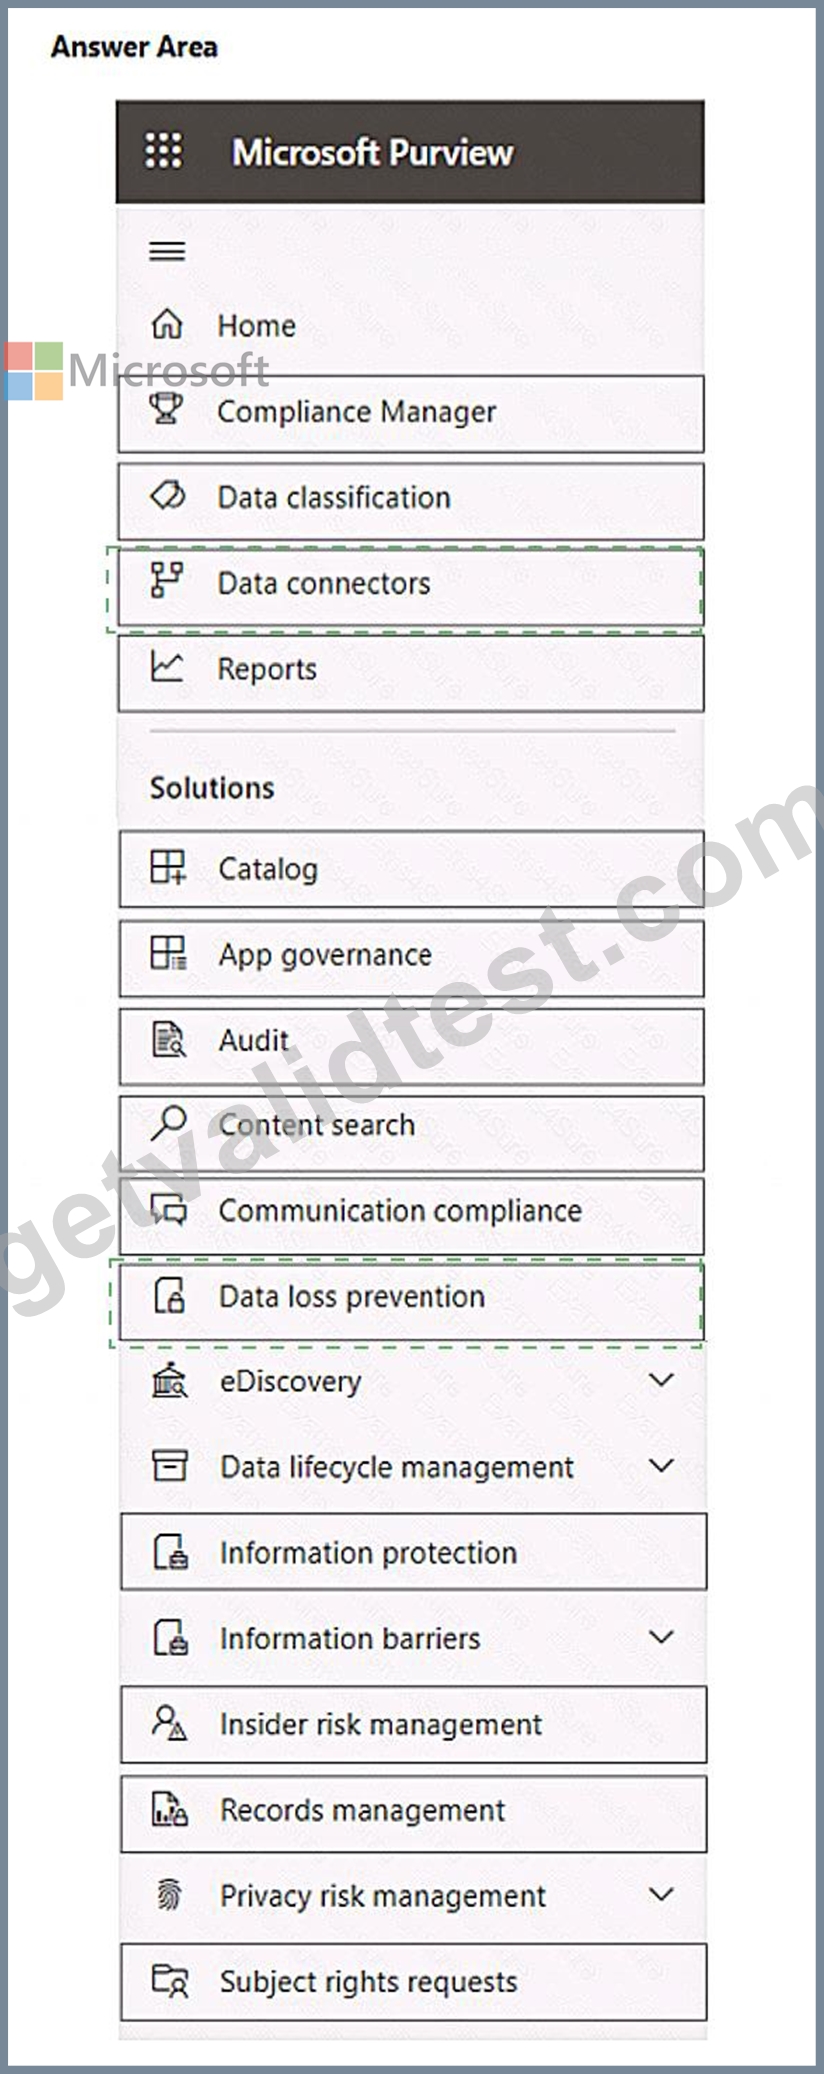
Explanation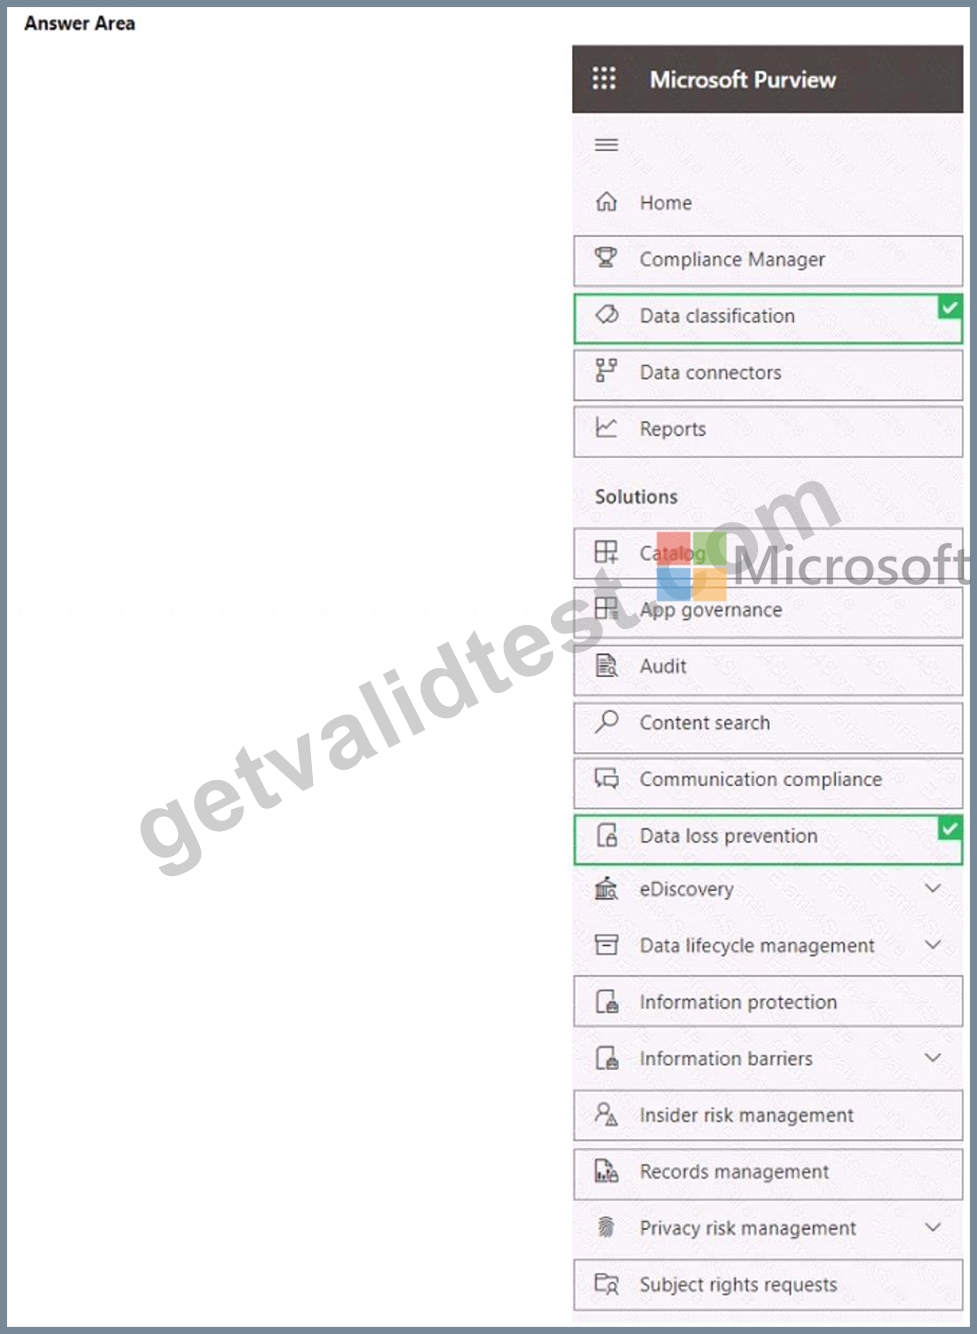
NEW QUESTION # 180
You have a Microsoft 365 tenant that contains the groups shown in the following table.
You plan to create a compliance policy named Compliance1.
You need to identify the groups that meet the following requirements:
Can be added to Compliance1 as recipients of noncompliance notifications Can be assigned to Compliance1 To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://www.itpromentor.com/devices-or-users-when-to-target-which-policy-type-in-microsoft-endpoint-manager-intune/
NEW QUESTION # 181
You are evaluating the required processes for Project1.
You need to recommend which DNS record must be created while adding a domain name for the project.
Which DNS record should you recommend?
- A. host information
- B. pointer (PTR)
- C. text (TXT)
- D. host (A)
Answer: D
Explanation:
Explanation
When you add a custom domain to Office 365, you need to verify that you own the domain. You can do this by adding either an MX record or a TXT record to the DNS for that domain.
Note:
There are several versions of this question in the exam. The question has two possible correct answers:
Text (TXT)
Mail exchanger (MX)
incorrect answer options you may see on the exam include the following:
alias (CNAME)
Host (A)
host (AAA)
Pointer (PTR)
Name Server (NS)
host information (HINFO)
pointer (PTR)
Reference:
https://docs.microsoft.com/en-us/office365/admin/get-help-with-domains/create-dns-records-at-any-dns-hosting-
NEW QUESTION # 182
Your company has a hybrid deployment of Microsoft 365.
An on-premises user named User1 is synced to Azure AD.
Azure AD Connect is configured as shown in the following exhibit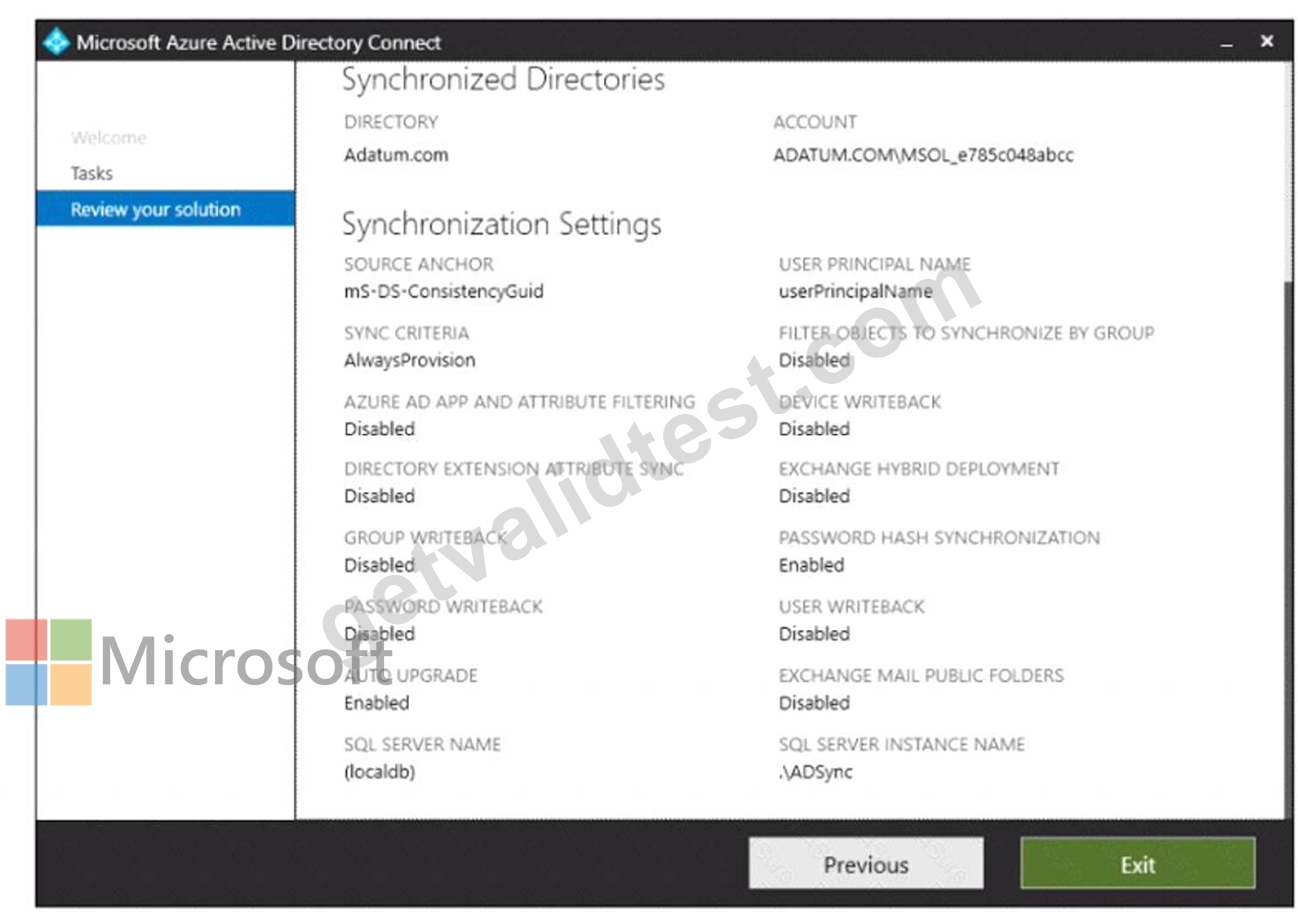
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.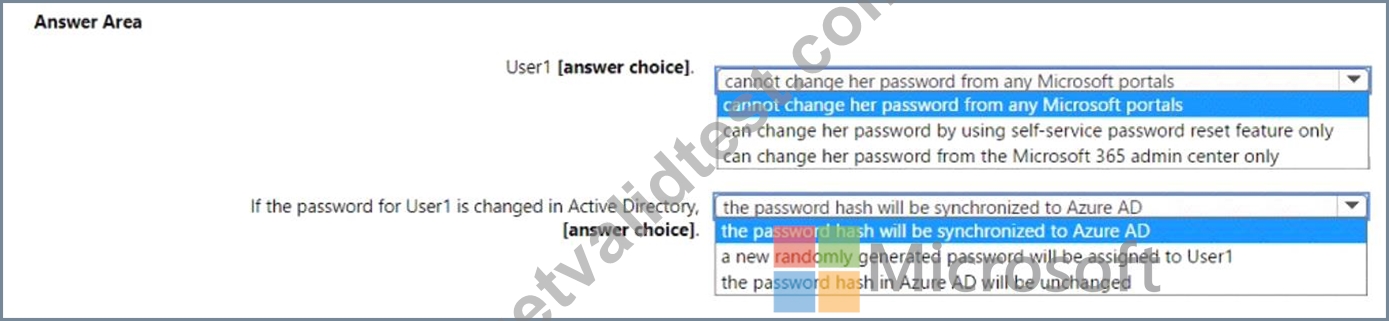
Answer:
Explanation:
Explanation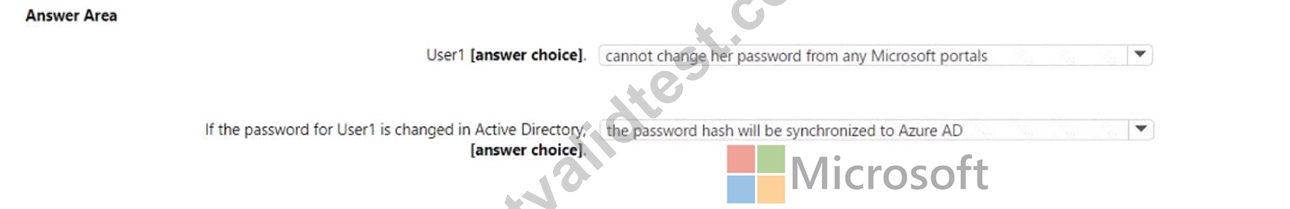
NEW QUESTION # 183
Your network contains an on-premises Active Directory domain. The domain contains the servers shown in the following table.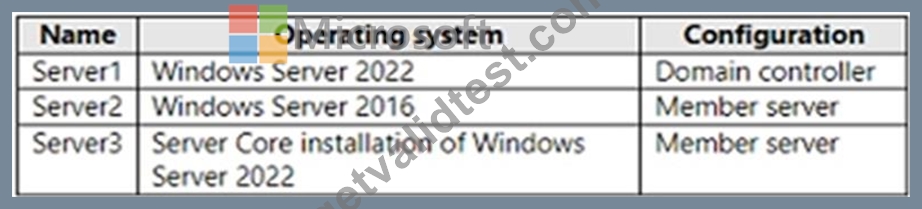
You purchase a Microsoft 365 E5 subscription.
You need to implement Azure AD Connect cloud sync.
What should you install first and on which server? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.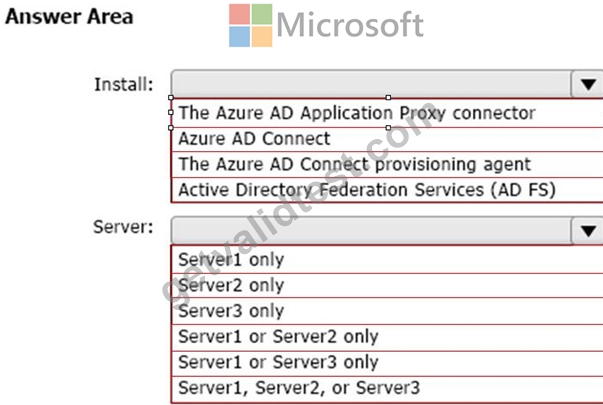
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/cloud-sync/how-to-install
https://docs.microsoft.com/en-us/azure/active-directory/cloud-sync/how-to-prerequisites
NEW QUESTION # 184
You have a Microsoft 365 E5 subscription that has published sensitivity labels shown in the following exhibit.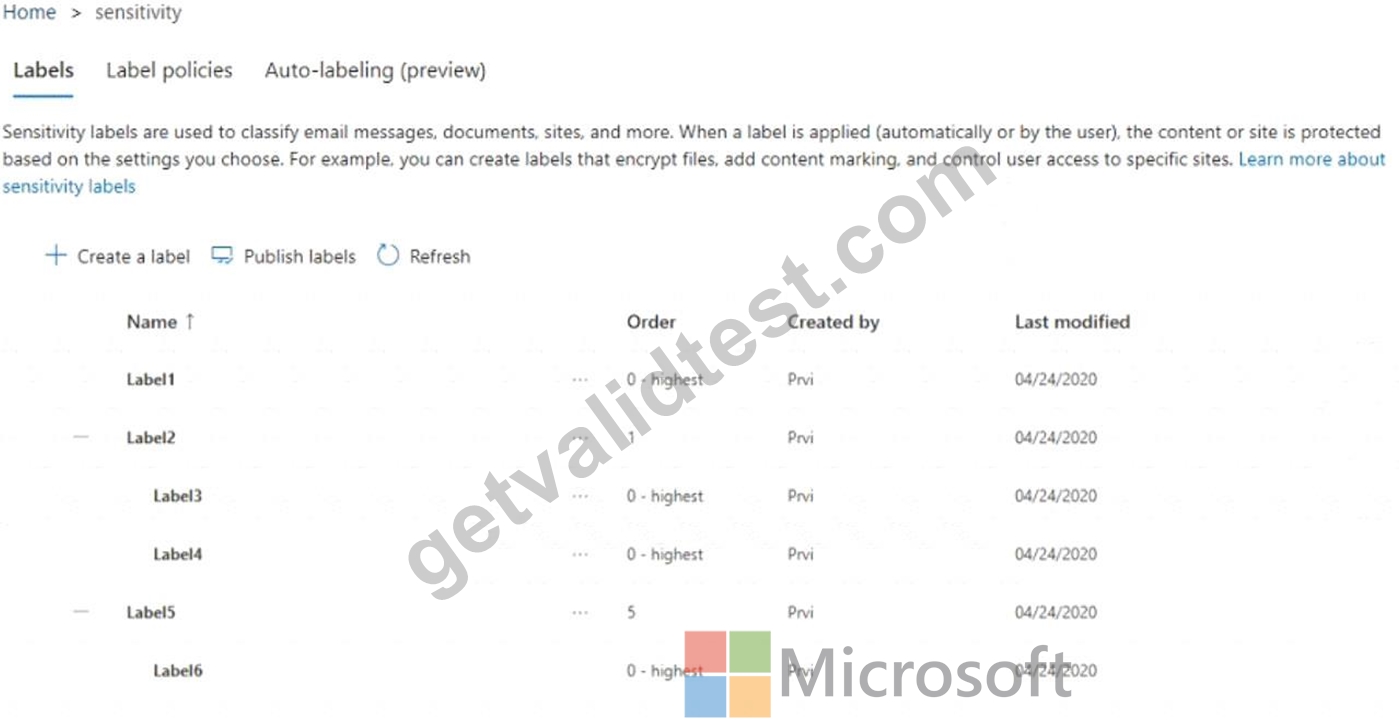
Which labels can users apply to content?
- A. Label1, Label2, Label3, Label4, Label5. and Label6
- B. Label1, Label2, and Label5 only
- C. Label1, Label3, Labe2, and Label6 only
- D. Label3. Label4, and Label6 only
Answer: C
NEW QUESTION # 185
You have a Microsoft 365 E5 tenant
You create a data toss prevention (DLP) policy to prevent users from using Microsoft Teams to share internal documents with external users.
To which two locations should you apply the policy? To answer, select the appropriate locations in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: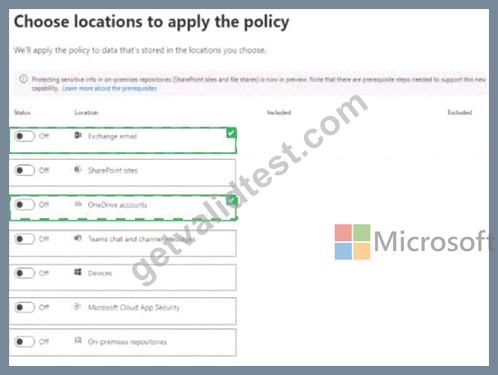
NEW QUESTION # 186
You have a new Microsoft 365 E5 tenant.
You need to enable an alert policy that will be triggered when an elevation of Microsoft Exchange Online administrative privileges is detected.
What should you do first?
- A. Create a communication compliance policy.
- B. Enable Microsoft 365 usage analytics.
- C. Create an Insider risk management policy.
- D. Enable auditing.
Answer: D
Explanation:
Microsoft Purview auditing solutions provide an integrated solution to help organizations effectively respond to security events, forensic investigations, internal investigations, and compliance obligations. Thousands of user and admin operations performed in dozens of Microsoft 365 services and solutions are captured, recorded, and retained in your organization's unified audit log. Audit records for these events are searchable by security ops, IT admins, insider risk teams, and compliance and legal investigators in your organization. This capability provides visibility into the activities performed across your Microsoft 365 organization.
Note: Permissions alert policies
Example: Elevation of Exchange admin privilege
Generates an alert when someone is assigned administrative permissions in your Exchange Online organization. For example, when a user is added to the Organization Management role group in Exchange Online.
Reference:
https://learn.microsoft.com/en-us/microsoft-365/compliance/audit-solutions-overview
https://learn.microsoft.com/en-us/microsoft-365/compliance/alert-policies
NEW QUESTION # 187
You have a Microsoft 365 E5 subscription that contains a user named User1 You create a retention label named Retention1 that is published to all locations.
You need to ensure that User1 can label email messages by using Retention1 as soon as possible.
Which cmdlet should you run in Microsoft Exchange Online PowerShell?
- A. Start-MpScan
- B. Start-AppBackgroundTask
- C. Start-ManagedFolderAsslstant
- D. Start-Process
Answer: C
NEW QUESTION # 188
You create the planned DLP policies.
You need to configure notifications to meet the technical requirements.
What should you do?
- A. From the Microsoft 365 compliance center, configure the Endpoint DLP settings.
- B. From the Microsoft 365 security center, configure an alert policy.
- C. From the Microsoft Endpoint Manager admin center, configure a custom notification.
- D. From the Microsoft 365 admin center, configure a Briefing email.
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/dlp-configure-view-alerts-policies?view=o365-worl
Topic 4, FabrikamOverview
Fabrikam, Inc. is an electronics company that produces consumer products. Fabrikam has 10,000 employees worldwide.
Fabrikam has a main office in London and branch offices in major cities in Europe, Asia, and the United States.
Existing Environment
Active Directory Environment
The network contains an Active Directory forest named fabrikam.com. The forest contains all the identities used for user and computer authentication. Each department is represented by a top-level organizational unit (OU) that contains several child OUs for user accounts and computer accounts.
All users authenticate to on-premises applications by signing in to their device by using a UPN format of [email protected].
Fabrikam does NOT plan to implement identity federation.
Network Infrastructure
Each office has a high-speed connection to the Internet.
Each office contains two domain controllers. All domain controllers are configured as DNS servers.
The public zone for fabrikam.com is managed by an external DNS server.
All users connect to an on-premises Microsoft Exchange Server 2016 organization. The users access their email by using Outlook Anywhere, Outlook on the web, or the Microsoft Outlook app for iOS. All the Exchange servers have the latest cumulative updates installed.
All shared company documents are stored on a Microsoft SharePoint Server farm.
Requirements
Planned Changes
Fabrikam plans to implement a Microsoft 365 Enterprise subscription and move all email and shared documents to the subscription.
Fabrikam plans to implement two pilot projects:
Project1: During Project1, the mailboxes of 100 users in the sales department will be moved to Microsoft 365.
Project2: After the successful completion of Project1, Microsoft Teams will be enabled in Microsoft 365 for the sales department users.
Fabrikam plans to create a group named UserLicenses that will manage the allocation of all Microsoft
365 bulk licenses.
Technical Requirements
Fabrikam identifies the following technical requirements:
All users must be able to exchange email messages successfully during Project1 by using their current email address.
Users must be able to authenticate to cloud services if Active Directory becomes unavailable.
A user named User1 must be able to view all DLP reports from the Microsoft Purview compliance portal.
Microsoft 365 Apps for enterprise applications must be installed from a network share only.
Disruptions to email access must be minimized.
Application Requirements
Fabrikam identifies the following application requirements:
An on-premises web application named App1 must allow users to complete their expense reports online.
App1 must be available to users from the My Apps portal.
The installation of feature updates for Microsoft 365 Apps for enterprise must be minimized.
Security Requirements
Fabrikam identifies the following security requirements:
After the planned migration to Microsoft 365, all users must continue to authenticate to their mailbox and to SharePoint sites by using their UPN.
The membership of the UserLicenses group must be validated monthly. Unused user accounts must be removed from the group automatically.
After the planned migration to Microsoft 365, all users must be signed in to on-premises and cloud-based applications automatically.
The principle of least privilege must be used.
NEW QUESTION # 189
You need to ensure that the support technicians can meet the technical requirement for the Montreal office mobile devices.
What is the minimum of dedicated support technicians required?
- A. 0
- B. 1
- C. 2
- D. 3
Answer: A
Explanation:
Explanation
References:
https://docs.microsoft.com/en-us/sccm/mdm/deploy-use/enroll-devices-with-device-enrollment-manager
NEW QUESTION # 190
You have a Microsoft 365 E5 subscription that uses Microsoft intune. The subscription contains the resources shown in the following table.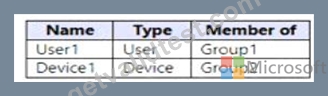
User1 is the owner of Device1.
You add Microsoft 365 Apps Windows 10 and later app types to Intune as shown in the following table.
On Thursday, you review the results of the app deployments.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.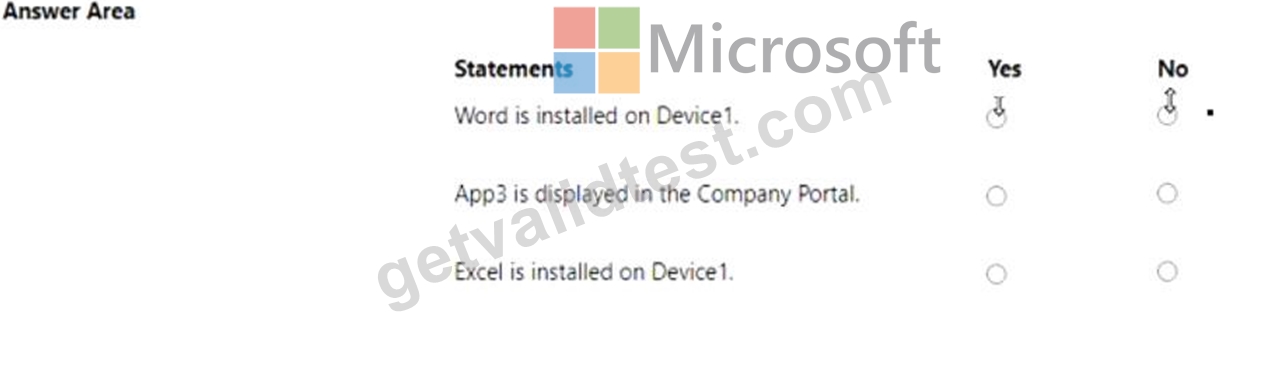
Answer:
Explanation: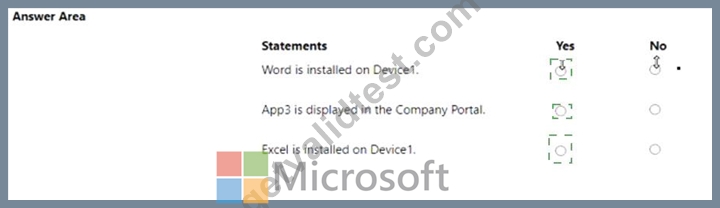
Explanation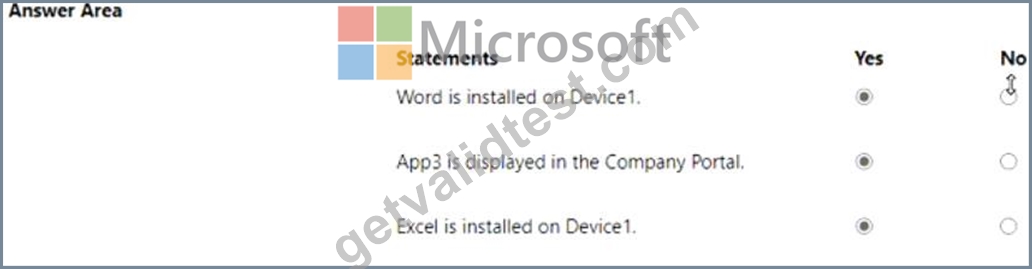
NEW QUESTION # 191
You have a Microsoft 365 E5 tenant.
You have a sensitivity label configured as shown in the Sensitivity label exhibit. (Click the Sensitivity label tab.)
You have an auto-labeling policy as shown in the Auto-labeling policy exhibit. (Click the Auto-labeling policy tab.)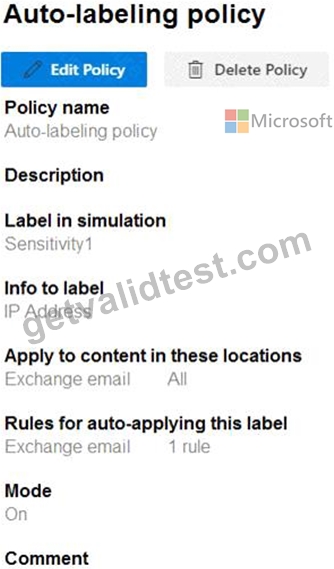
A user sends an email that contains the components shown in the following table.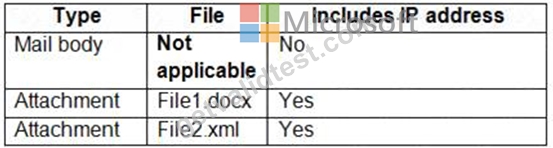
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.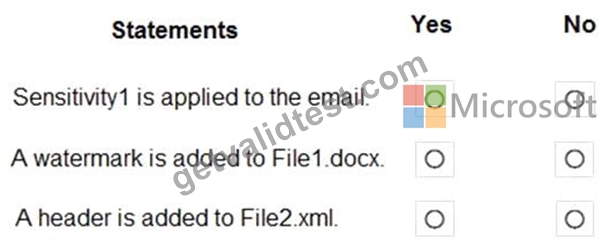
Answer:
Explanation: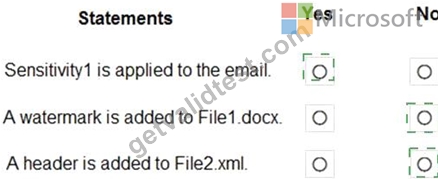
Explanation
Graphical user interface, text, application Description automatically generated
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/apply-sensitivity-label-automatically?view=o365-wo
NEW QUESTION # 192
HOTSPOT
You have a Microsoft 365 subscription.
You are planning a threat management solution for your organization.
You need to minimize the likelihood that users will be affected by the following threats:
Which policies should you create in Microsoft 365 Defender? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
- A. Opening files in Microsoft SharePoint that contain malicious content
- B. Impersonation and spoofing attacks in email messages
Answer: A
Explanation:
Explanation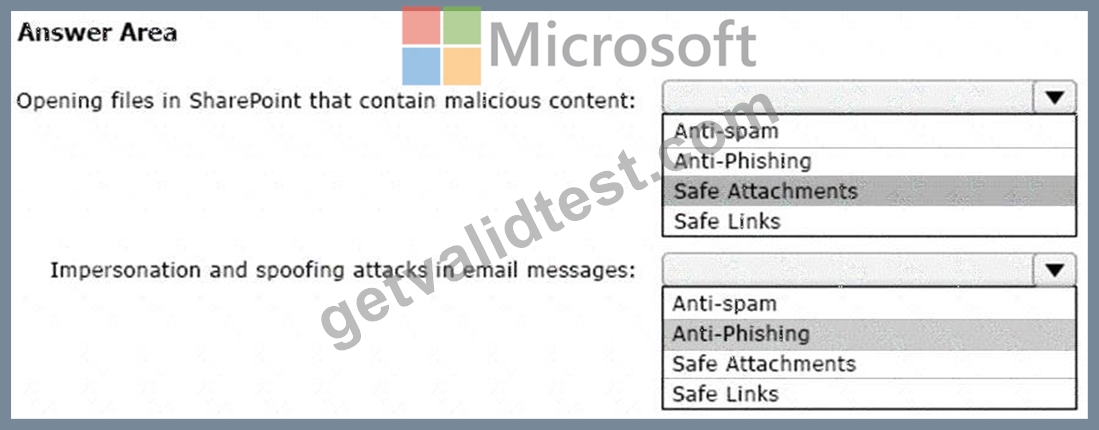
NEW QUESTION # 193
......
MS-102 dumps Free Test Engine Verified By It Certified Experts: https://www.getvalidtest.com/MS-102-exam.html
View All MS-102 Actual Exam Questions, Answers and Explanations for Free: https://drive.google.com/open?id=1M2f1L-KrIKvCTo7WeolhrrW18wicIZ1R