


[Oct-2021] Valid Way To Pass Cisco Exam Dumps with 300-710 Exam Study Guide
All 300-710 Dumps and Securing Networks with Cisco Firepower Training Courses Help candidates to study and pass the Exams hassle-free!
NEW QUESTION 40
Which Cisco Advanced Malware Protection for Endpoints policy is used only for monitoring endpoint actively?
- A. audit
- B. Windows domain controller
- C. triage
- D. protection
Answer: A
NEW QUESTION 41
Which two types of objects are reusable and supported by Cisco FMC? (Choose two.)
- A. reputation-based objects, such as URL categories
- B. network-based objects that represent FQDN mappings and networks, port/protocol pairs, VXLAN tags, security zones and origin/destination country
- C. network-based objects that represent IP address and networks, port/protocols pairs, VLAN tags, security zones, and origin/destination country
- D. dynamic key mapping objects that help link HTTP and HTTPS GET requests to Layer 7 application protocols.
- E. reputation-based objects that represent Security Intelligence feeds and lists, application filters based on category and reputation, and file lists
Answer: C,E
NEW QUESTION 42
What is the maximum bit size that Cisco FMC supports for HTTPS certificates?
- A. 0
- B. 1
- C. 2
- D. 3
Answer: B
Explanation:
Reference: https://www.cisco.com/c/en/us/td/docs/security/firepower/610/configuration/guide/fpmc-config-guide-v61/system_configuration.html
NEW QUESTION 43
Which CLI command is used to control special handling of ClientHello messages?
- A. system support ssl-client-hello-reset
- B. system support ssl-client-hello-display
- C. system support ssl-client-hello-force-reset
- D. system support ssl-client-hello-tuning
Answer: D
Explanation:
Section: Management and Troubleshooting
Explanation/Reference: https://www.cisco.com/c/en/us/td/docs/security/firepower/610/configuration/guide/fpmc-config- guide-v61/firepower_command_line_reference.html
NEW QUESTION 44
An organization is setting up two new Cisco FTD devices to replace their current firewalls and cannot have any network downtime During the setup process, the synchronization between the two devices is failing What action is needed to resolve this issue?
- A. Confirm that both devices have the same flash memory sizes
- B. Confirm that both devices are configured with the same types of interfaces
- C. Confirm that both devices have the same port-channel numbering
- D. Confirm that both devices are running the same software version
Answer: D
NEW QUESTION 45
A network administrator is configuring Snort inspection policies and is seeing failed deployment messages in Cisco FMC. What information should the administrator generate for Cisco TAC to help troubleshoot?
- A. A "troubleshoot" file for the device in question.
- B. A "show tech" file for the device in question.
- C. A "troubleshoot" file for the Cisco FMC.
- D. A "show tech" for the Cisco FMC.
Answer: A
NEW QUESTION 46
Which group within Cisco does the Threat Response team use for threat analysis and research?
- A. Cisco Network Response
- B. Cisco Talos
- C. OpenDNS Group
- D. Cisco Deep Analytics
Answer: B
Explanation:
Reference:
https://www.cisco.com/c/en/us/products/security/threat-response.html#~benefits
NEW QUESTION 47
Which action should be taken after editing an object that is used inside an access control policy?
- A. Refresh the Cisco FMC GUI for the access control policy.
- B. Redeploy the updated configuration.
- C. Delete the existing object in use.
- D. Create another rule using a different object name.
Answer: B
Explanation:
Reference: https://www.cisco.com/c/en/us/td/docs/security/firepower/630/configuration/guide/fpmc-config-guide-v63/reusable_objects.html
NEW QUESTION 48
Refer to the exhibit.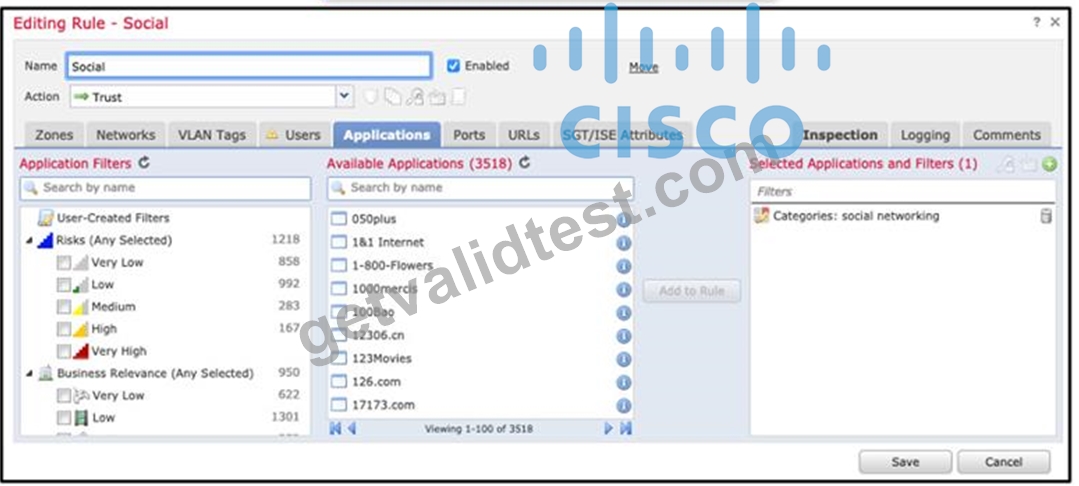
An organization has an access control rule with the intention of sending all social media traffic for inspection After using the rule for some time, the administrator notices that the traffic is not being inspected, but is being automatically allowed What must be done to address this issue?
- A. Modify the rule action from trust to allow
- B. Change the intrusion policy to connectivity over security.
- C. Add the social network URLs to the block list
- D. Modify the selected application within the rule
Answer: D
NEW QUESTION 49
What is a behavior of a Cisco FMC database purge?
- A. The specified data is removed from Cisco FMC and kept for two weeks.
- B. User login and history data are removed from the database if the User Activity check box is selected.
- C. The appropriate process is restarted.
- D. Data can be recovered from the device.
Answer: C
NEW QUESTION 50
A security engineer is configuring an Access Control Policy for multiple branch locations These locations share a common rule set and utilize a network object called INSIDE_NET which contains the locally significant internal network subnets at each location What technique will retain the policy consistency at each location but allow only the locally significant network subnet within the applicable rules?
- A. utilizing policy inheritance
- B. creating a unique ACP per device
- C. utilizing a dynamic ACP that updates from Cisco Talos
- D. creating an ACP with an INSIDE_NET network object and object overrides
Answer: A
NEW QUESTION 51
An engineer is attempting to add a new FTD device to their FMC behind a NAT device with a NAT ID of ACME001 and a password of Cisco388267669. Which command set must be used in order to accomplish this?
- A. configure manager add ACME001 <registration key> <FMC IP>
- B. configure manager add <FMC IP> registration key> ACME001
- C. configure manager add DONTRESOLVE <FMC IP> AMCE001 <registration key>
- D. configure manager add <FMC IP> ACME0O1 <registration key>
Answer: B
NEW QUESTION 52
Which protocol establishes network redundancy in a switched Firepower device deployment?
- A. STP
- B. HSRP
- C. GLBP
- D. VRRP
Answer: A
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/firepower/620/configuration/guide/fpmc-config- guide-v62/firepower_threat_defense_high_availability.html
NEW QUESTION 53
Which CLI command is used to control special handling of ClientHello messages?
- A. system support ssl-client-hello-display
- B. system support ssl-client-hello-force-reset
- C. system support ssl-client-hello-enabled
- D. system support ssl-client-hello-tuning
Answer: D
NEW QUESTION 54
A security engineer is configuring an Access Control Policy for multiple branch locations These locations share a common rule set and utilize a network object called INSIDE_NET which contains the locally significant internal network subnets at each location What technique will retain the policy consistency at each location but allow only the locally significant network subnet within the applicable rules?
- A. utilizing policy inheritance
- B. creating an ACP with an INSIDE_NET network object and object overrides
- C. creating a unique ACP per device
- D. utilizing a dynamic ACP that updates from Cisco Talos
Answer: B
NEW QUESTION 55
Which two remediation options are available when Cisco FMC is integrated with Cisco ISE? (Choose two.)
- A. dynamic null route configured
- B. host shutdown
- C. quarantine
- D. port shutdown
- E. DHCP pool disablement
Answer: C,D
Explanation:
Reference:
https://www.cisco.com/c/en/us/support/docs/security/identity-services-engine/210524-configure- firepower-6-1-pxgrid-remediati.html
NEW QUESTION 56
Which policy rule is included in the deployment of a local DMZ during the initial deployment of a Cisco NGFW through the Cisco FMC GUI?
- A. a default DMZ policy for which only a user can change the IP addresses.
- B. deny ip any
- C. permit ip any
- D. no policy rule is included
Answer: D
NEW QUESTION 57
When do you need the file-size command option during troubleshooting with packet capture?
- A. when capture packets are less than 16 MB
- B. when capture packets exceed 32 MB
- C. when capture packets exceed 10 GB
- D. when capture packets are restricted from the secondary memory
Answer: B
Explanation:
Section: Management and Troubleshooting
Explanation/Reference: https://www.cisco.com/c/en/us/td/docs/security/firepower/620/configuration/guide/fpmc-config- guide-v62/troubleshooting_the_system.html
NEW QUESTION 58
Which two statements about bridge-group interfaces in Cisco FTD are true? (Choose two.)
- A. Bridge groups are supported only in transparent firewall mode.
- B. Bidirectional Forwarding Detection echo packets are allowed through the FTD when using bridge-group members.
- C. Each directly connected network must be on the same subnet.
- D. Bridge groups are supported in both transparent and routed firewall modes.
- E. The BVI IP address must be in a separate subnet from the connected network.
Answer: A,B
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/firepower/620/configuration/guide/fpmc-config- guide-v62/transparent_or_routed_firewall_mode_for_firepower_threat_defense.html
NEW QUESTION 59
When do you need the file-size command option during troubleshooting with packet capture?
- A. when capture packets are less than 16 MB
- B. when capture packets exceed 32 MB
- C. when capture packets exceed 10 GB
- D. when capture packets are restricted from the secondary memory
Answer: B
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/firepower/620/configuration/guide/fpmc-config- guide-v62/troubleshooting_the_system.html
NEW QUESTION 60
In which two places can thresholding settings be configured? (Choose two.)
- A. per preprocessor, within the network analysis policy
- B. on each access control rule
- C. globally, within the network analysis policy
- D. globally, per intrusion policy
- E. on each IPS rule
Answer: D,E
NEW QUESTION 61
......
Real Exam Questions & Answers - Cisco 300-710 Dump is Ready: https://drive.google.com/open?id=1f4sqIiCCsC-rLqRcCCQQ0pE4jbgh9GXQ
Get Latest [Oct-2021] Conduct effective penetration tests using GetValidTest 300-710